This page is the written version of the presentation we use to introduce SanctumShield. It follows the slides in order, so you can read it in a few minutes or page through the pictures.
The question
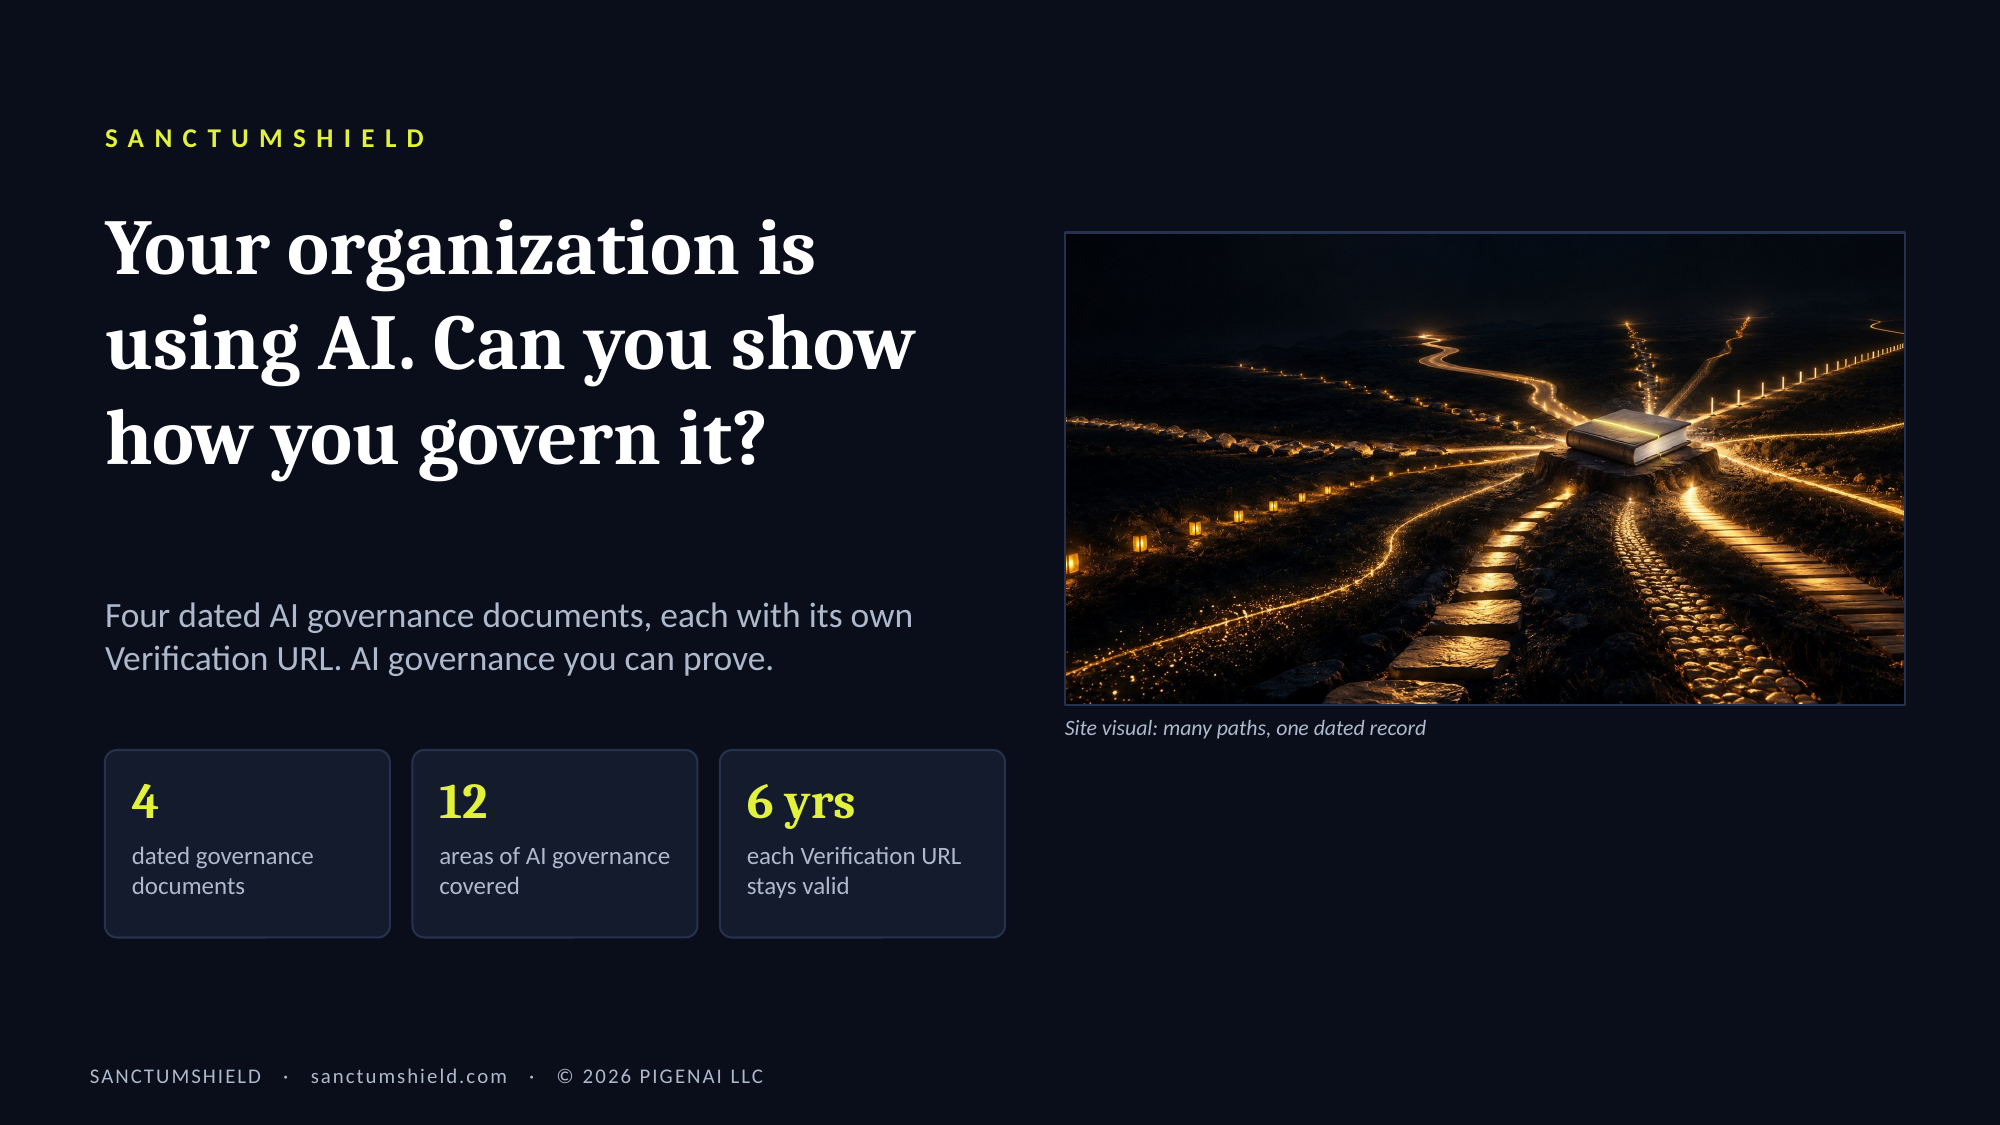
Most organizations now use AI every day. The question boards, auditors and insurers have started to ask is a simple one: can you show how you govern it?
A useful answer has three parts. Where is AI already working in your organization, including the tools on personal logins and the AI built into software you already pay for? What is each tool and agent allowed to do, and who agreed? And what dated record shows what you assessed and decided?
Why now
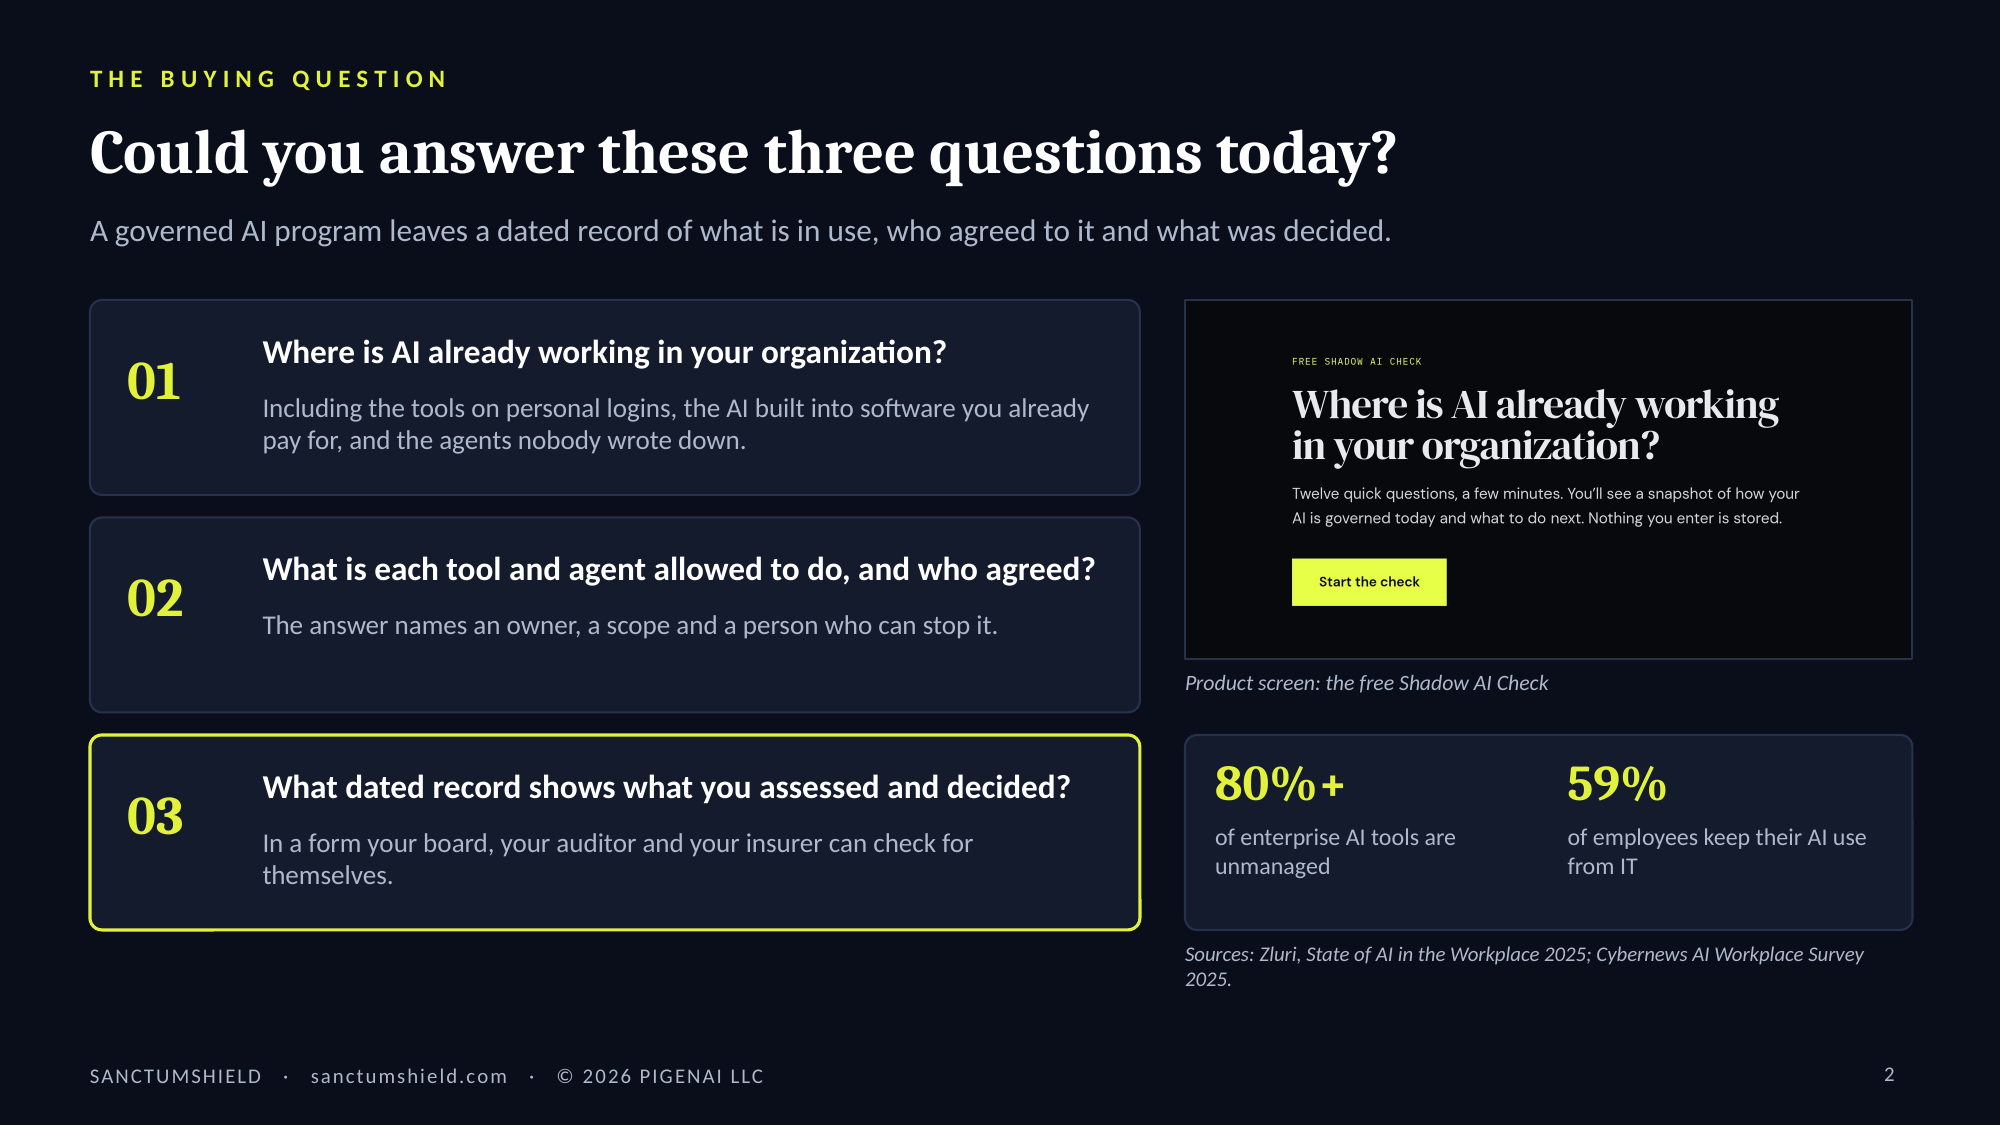
The dates are already on the calendar. The EU AI Act's Article 4 AI literacy duty has applied since February 2, 2025, and its Article 50 transparency obligations since August 2, 2026. Colorado SB 26-189 was signed May 14, 2026, with duties from January 1, 2027. The EU AI Act's high-risk obligations follow on December 2, 2027 and August 2, 2028.
Each of these expects the same kind of thing: a policy, a documented risk assessment, and a dated record of who decided what.
Three layers, three records
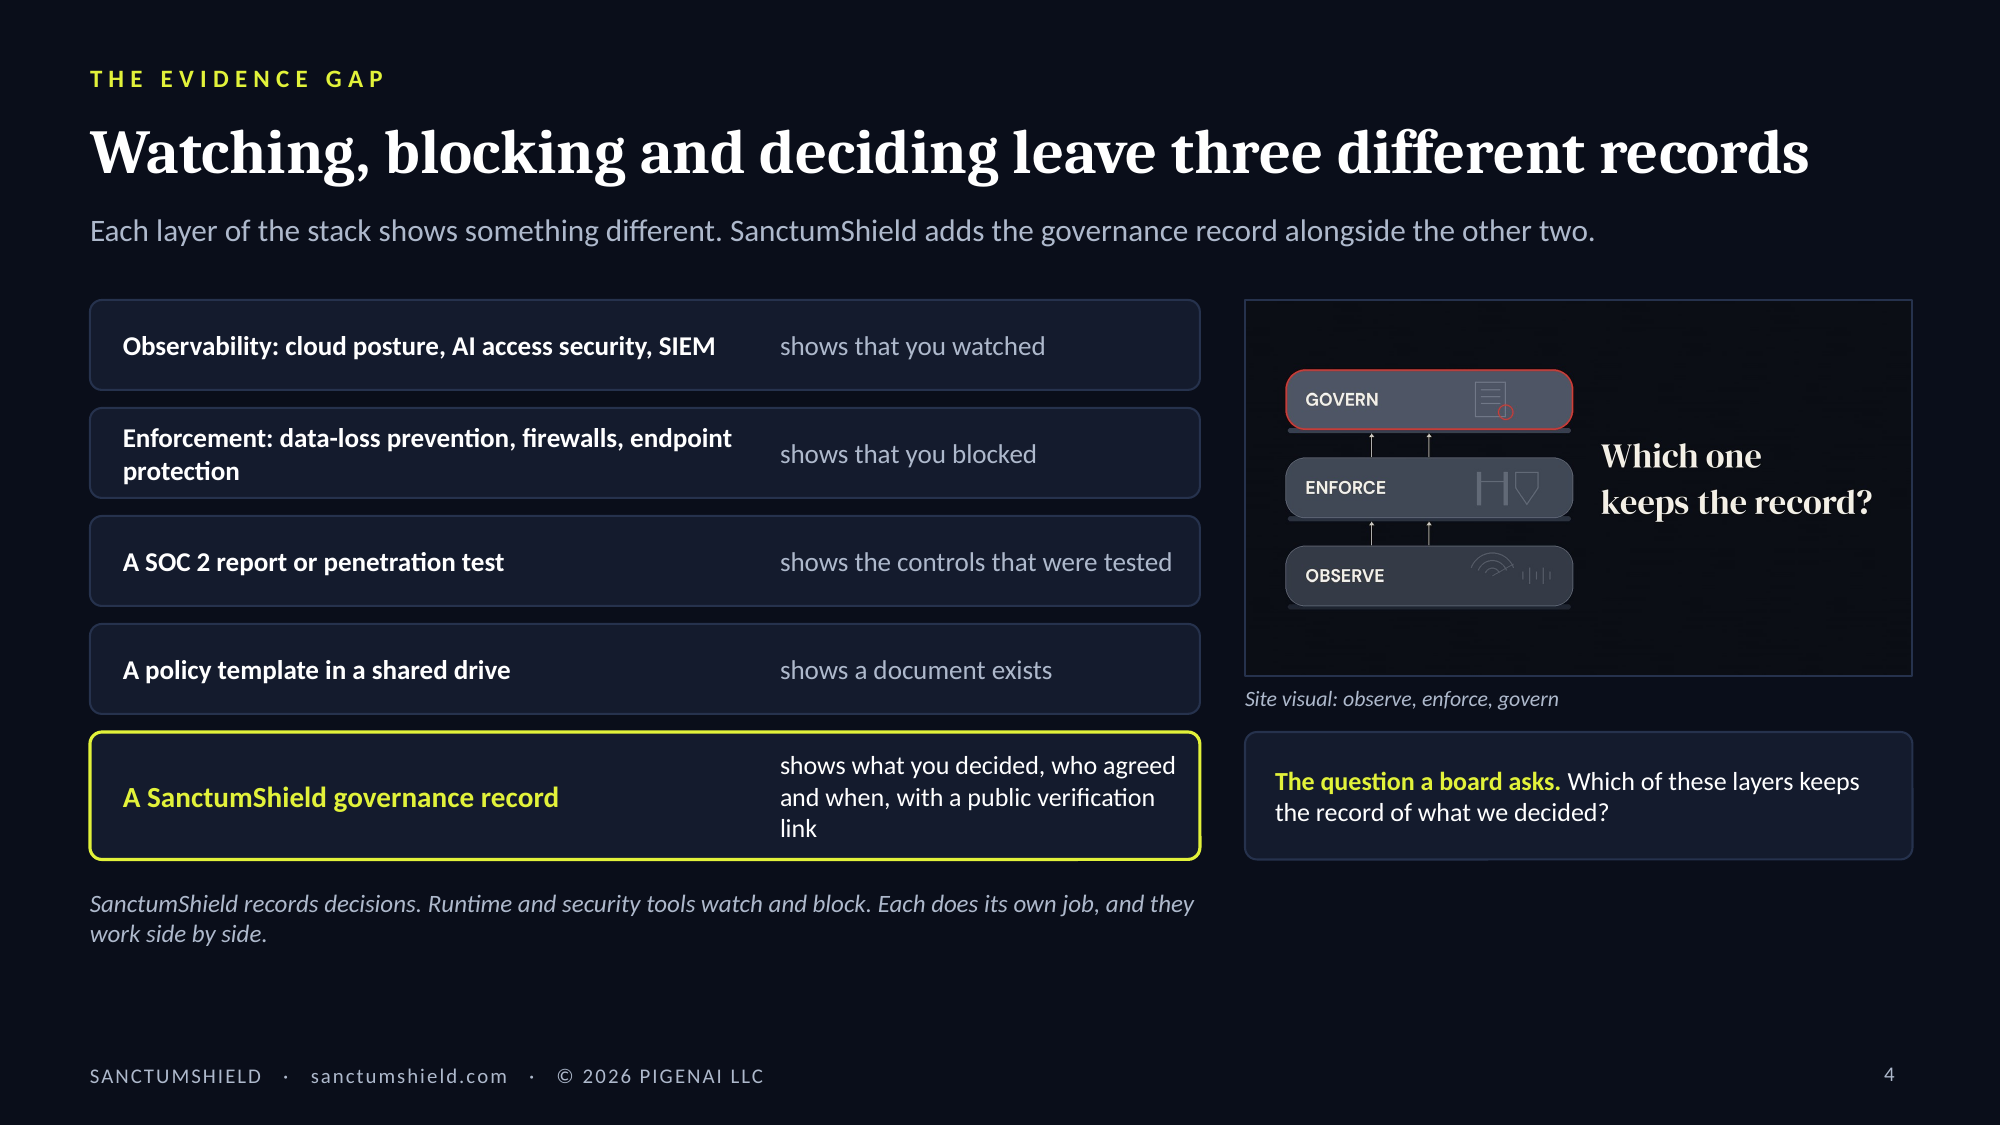
A modern security stack does several jobs well. Observability tools show that you watched. Enforcement tools show that you blocked. A governance record shows what you decided, who agreed and when.
SanctumShield adds that third record. It works alongside the tools you already run, and each one keeps doing its own job.
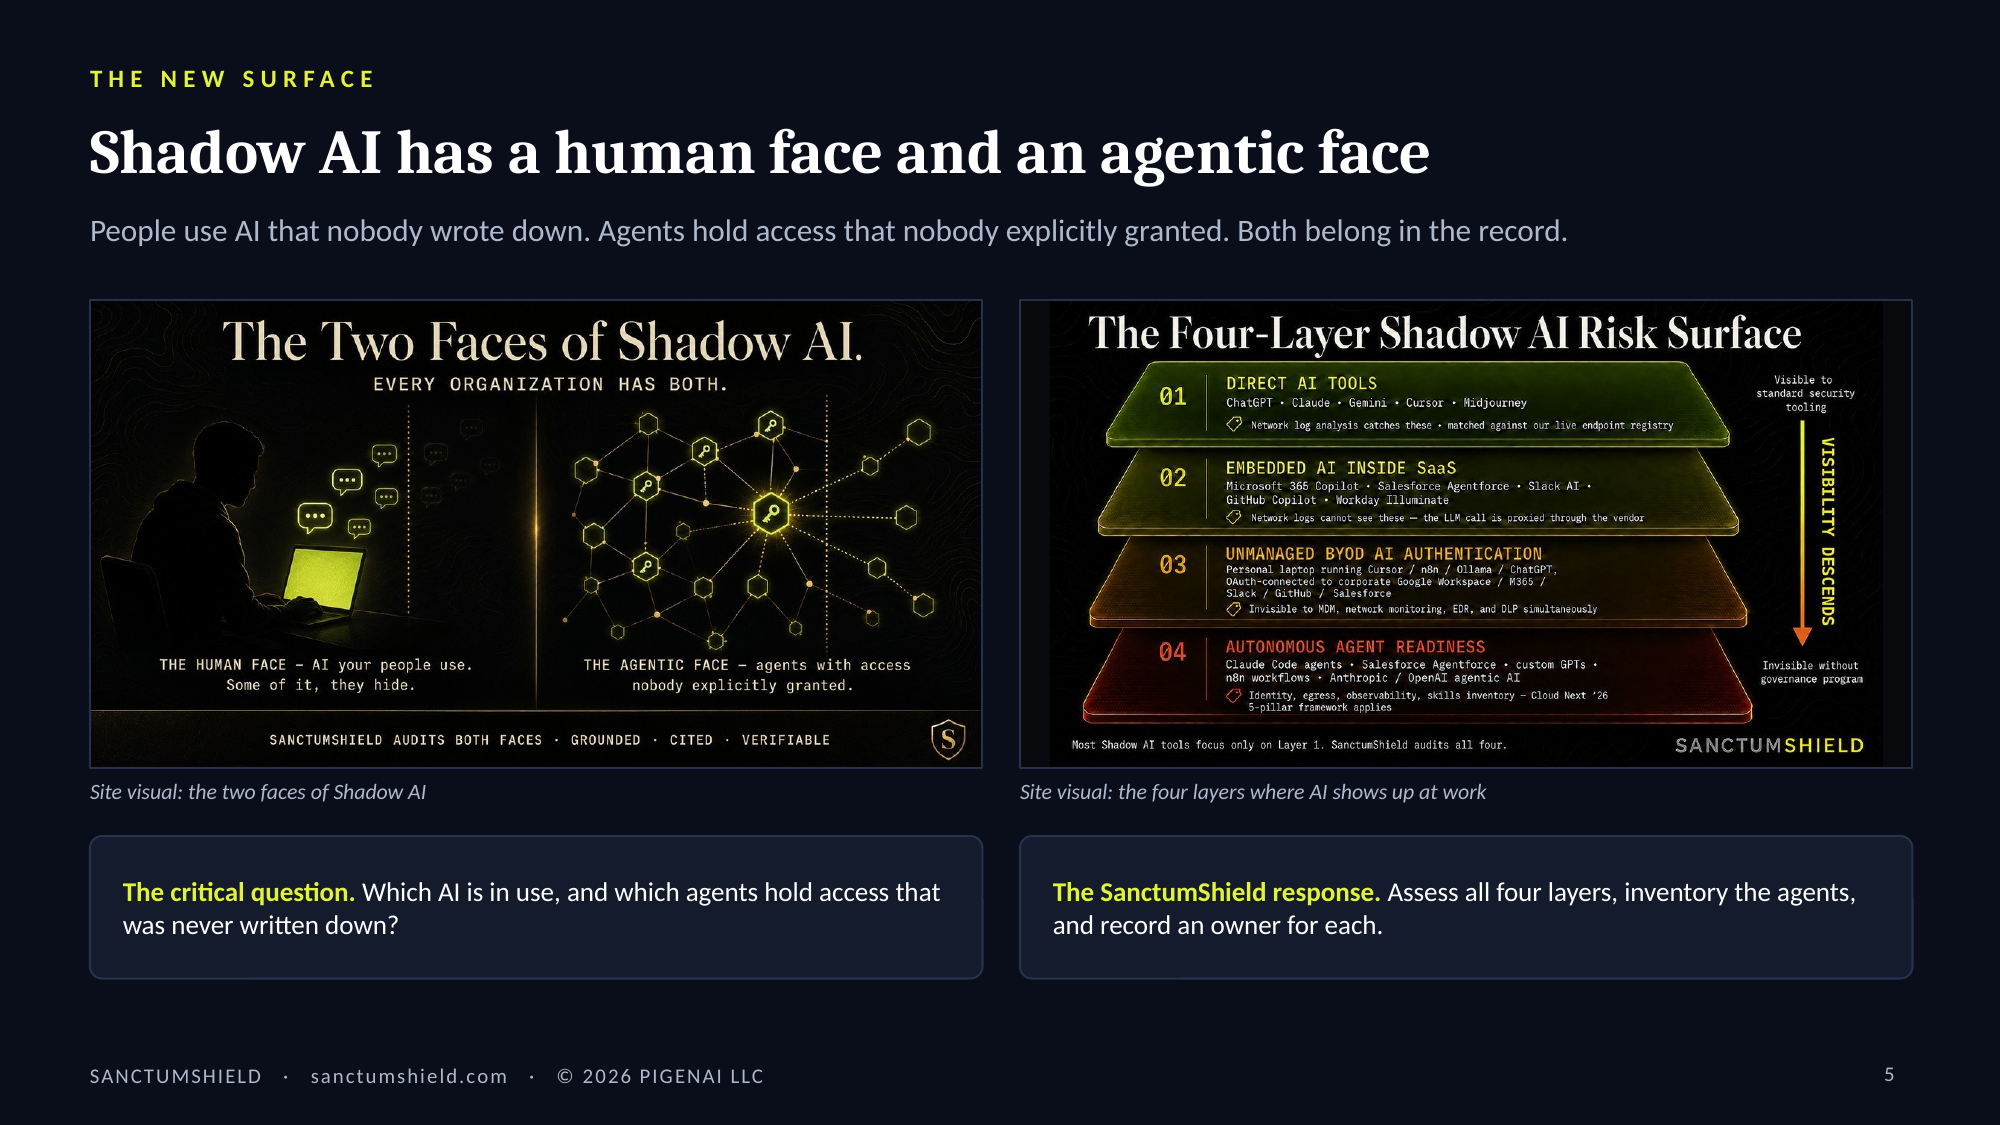
The two faces of Shadow AI
AI shows up at work in two ways. People use tools that nobody wrote down. Agents hold access that nobody explicitly granted. Both belong in the record, so the review looks at four layers: direct AI tools, AI built into business software, AI on personal and unmanaged devices, and autonomous agents.
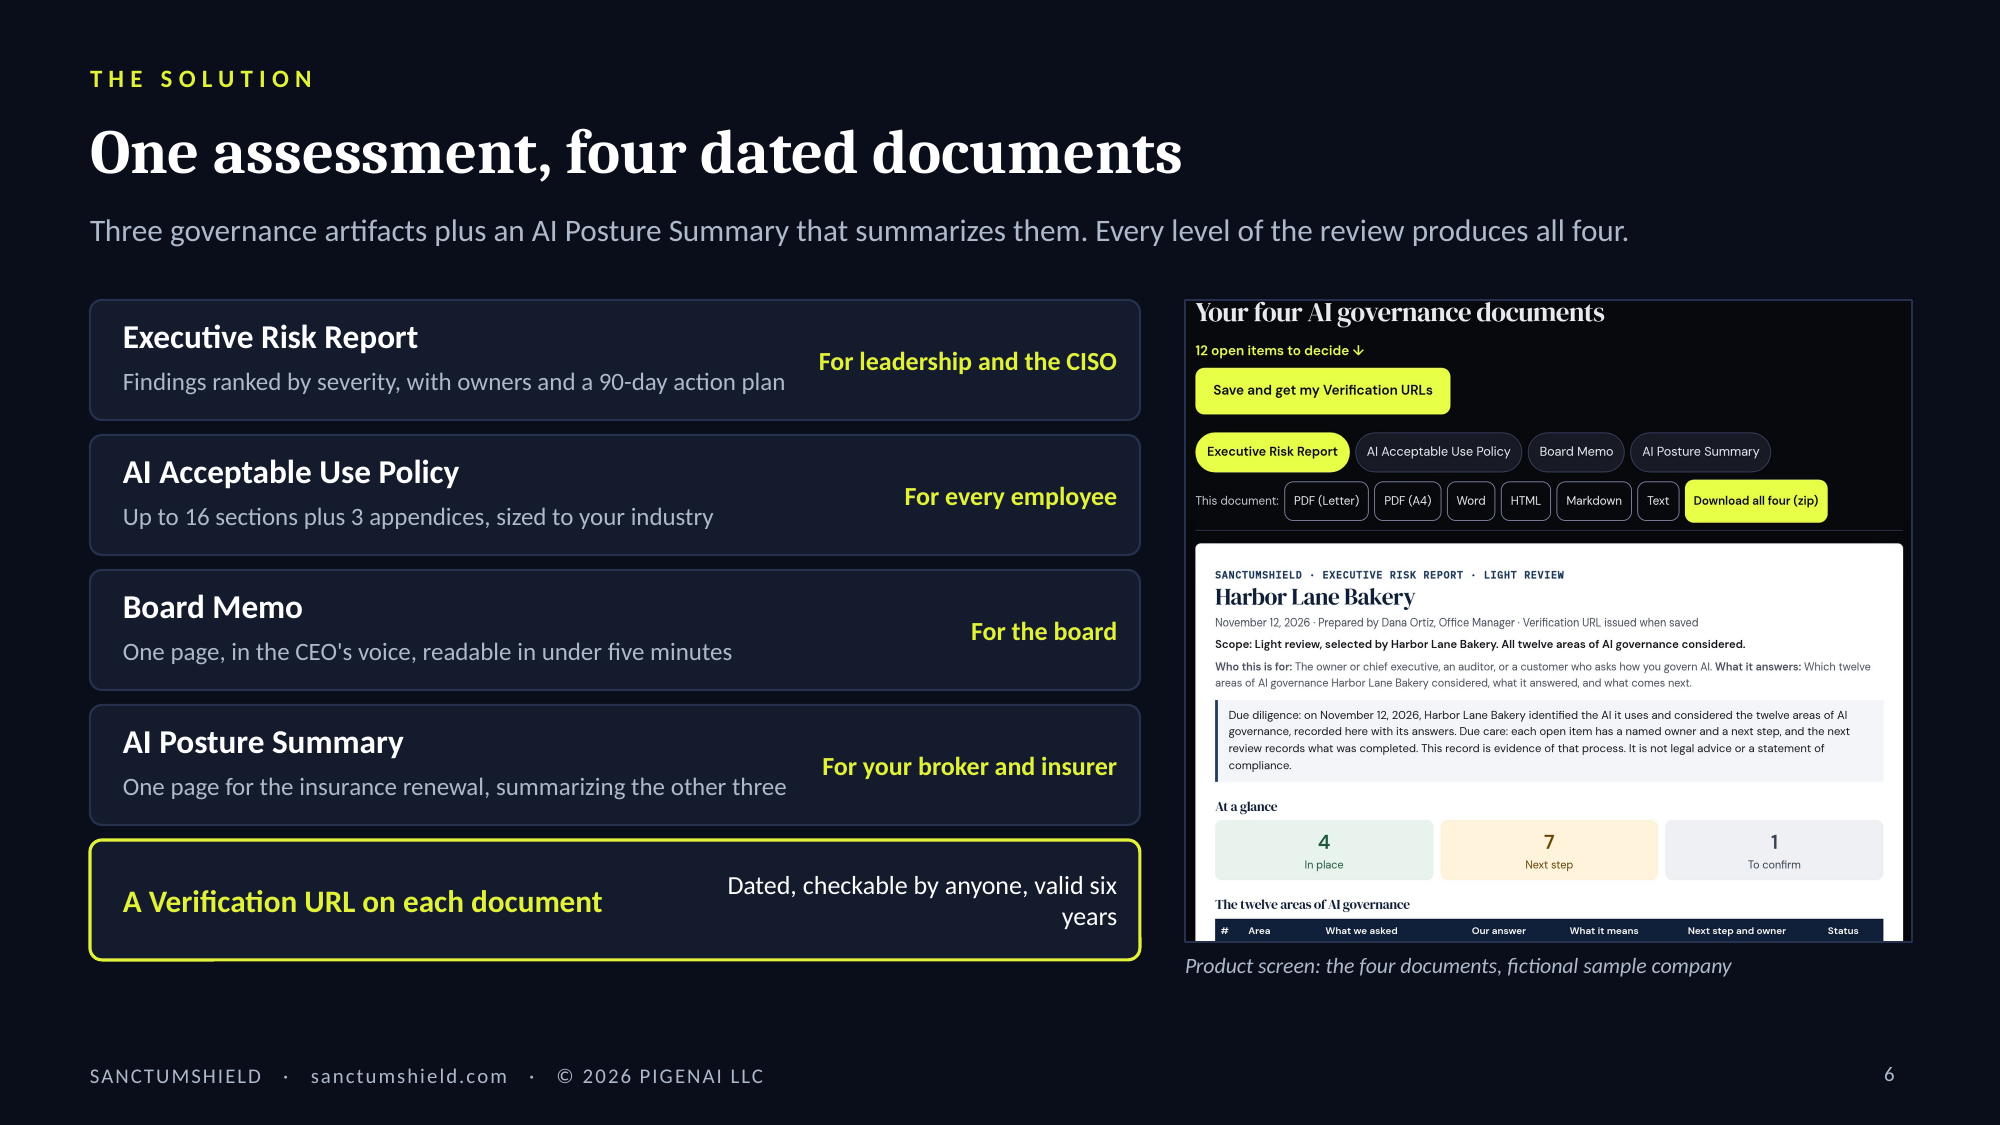
One assessment, four dated documents
One guided review produces four documents:
- Executive Risk Report. Findings ranked by severity, with owners and a 90-day action plan.
- AI Acceptable Use Policy. Sized to your industry, your jurisdictions and the frameworks you name.
- Board Memo. One page, in the CEO's voice.
- AI Posture Summary. One page for the insurance renewal, summarizing the other three.
Each document carries its own Verification URL.
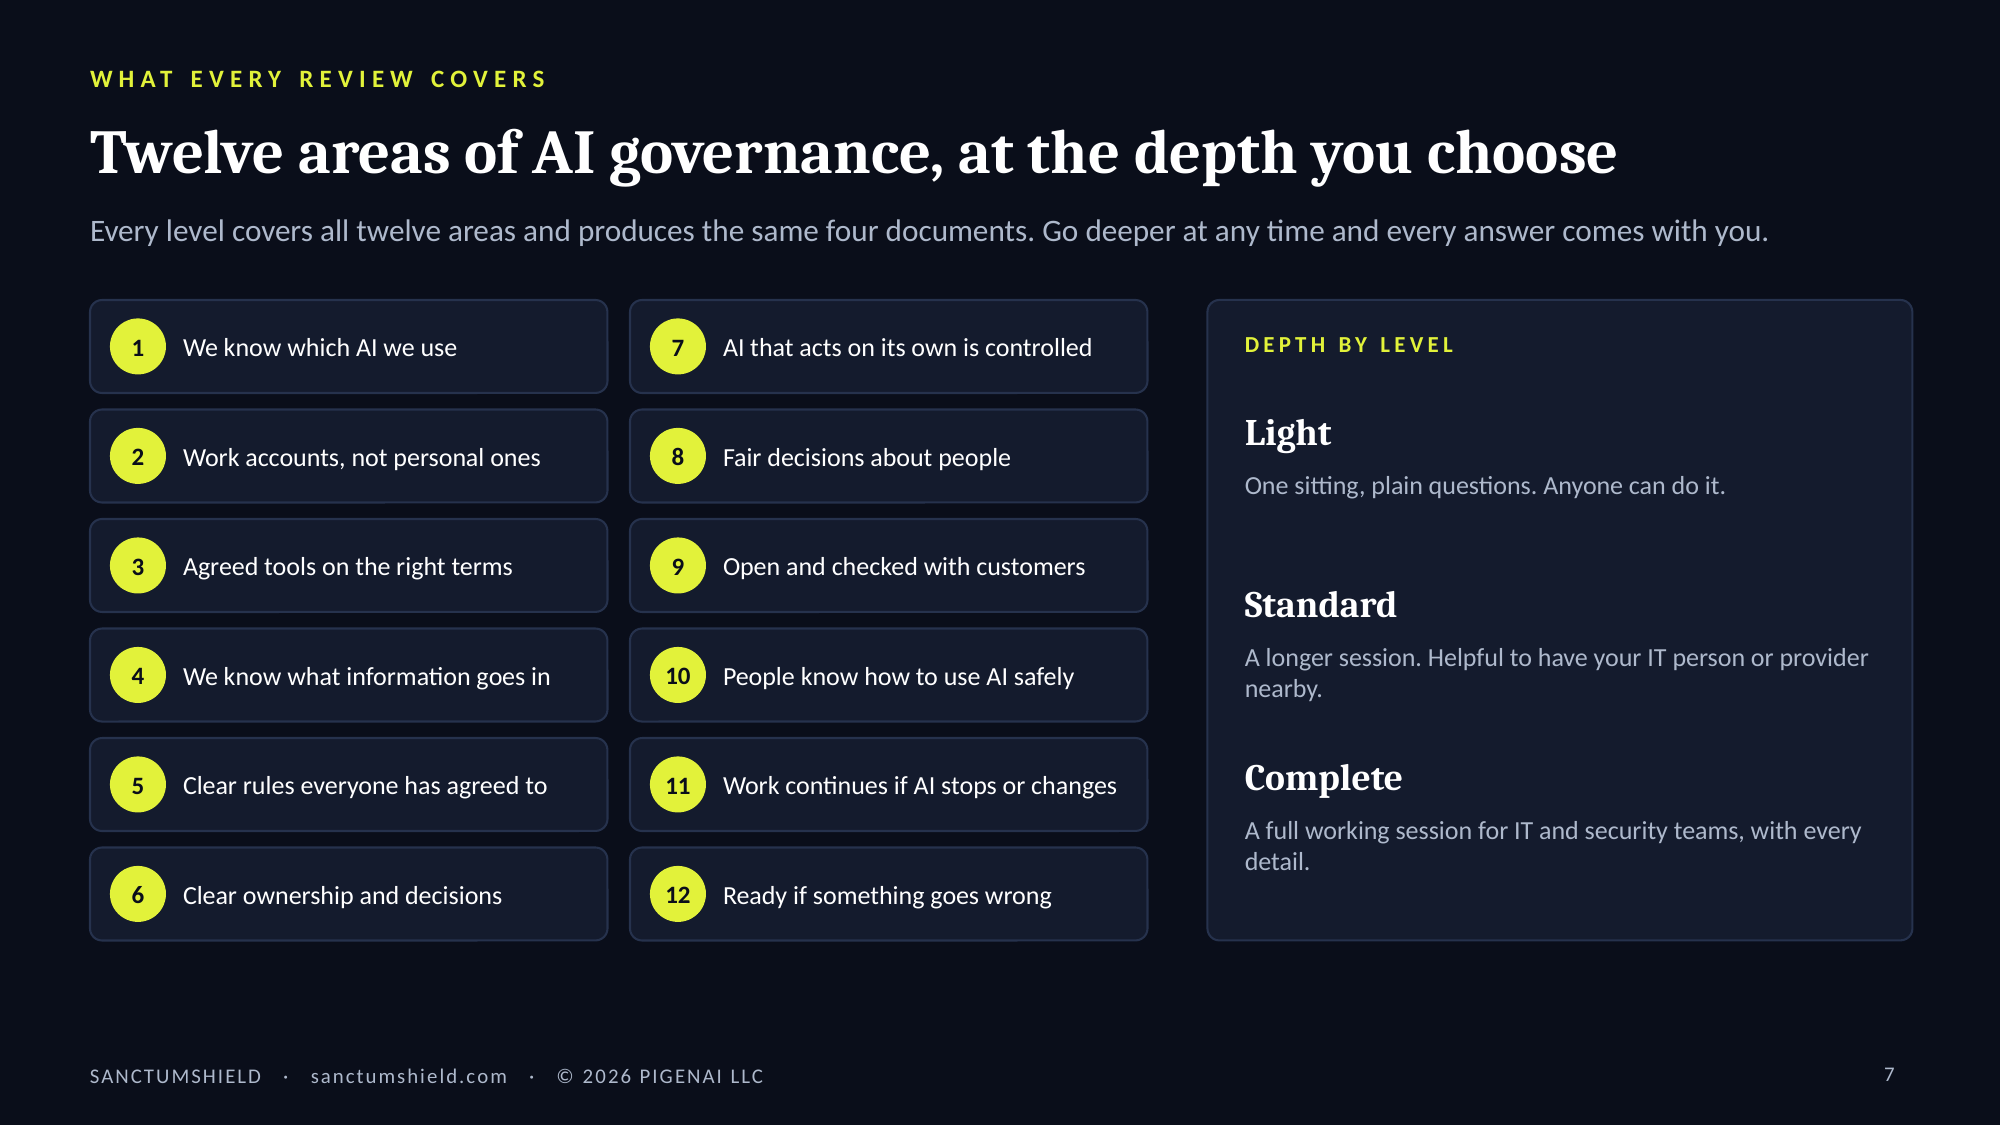
Twelve areas, at the depth you choose
Every review covers the same twelve areas of AI governance, in plain words: from "We know which AI we use" to "Ready if something goes wrong."
You choose the depth. Light is one sitting with plain questions. Standard is a longer session, helpful with your IT person or provider nearby. Complete is a full working session for IT and security teams. Every level produces the same four documents, and you can go deeper at any time with every answer carried forward.
What the review is grounded in
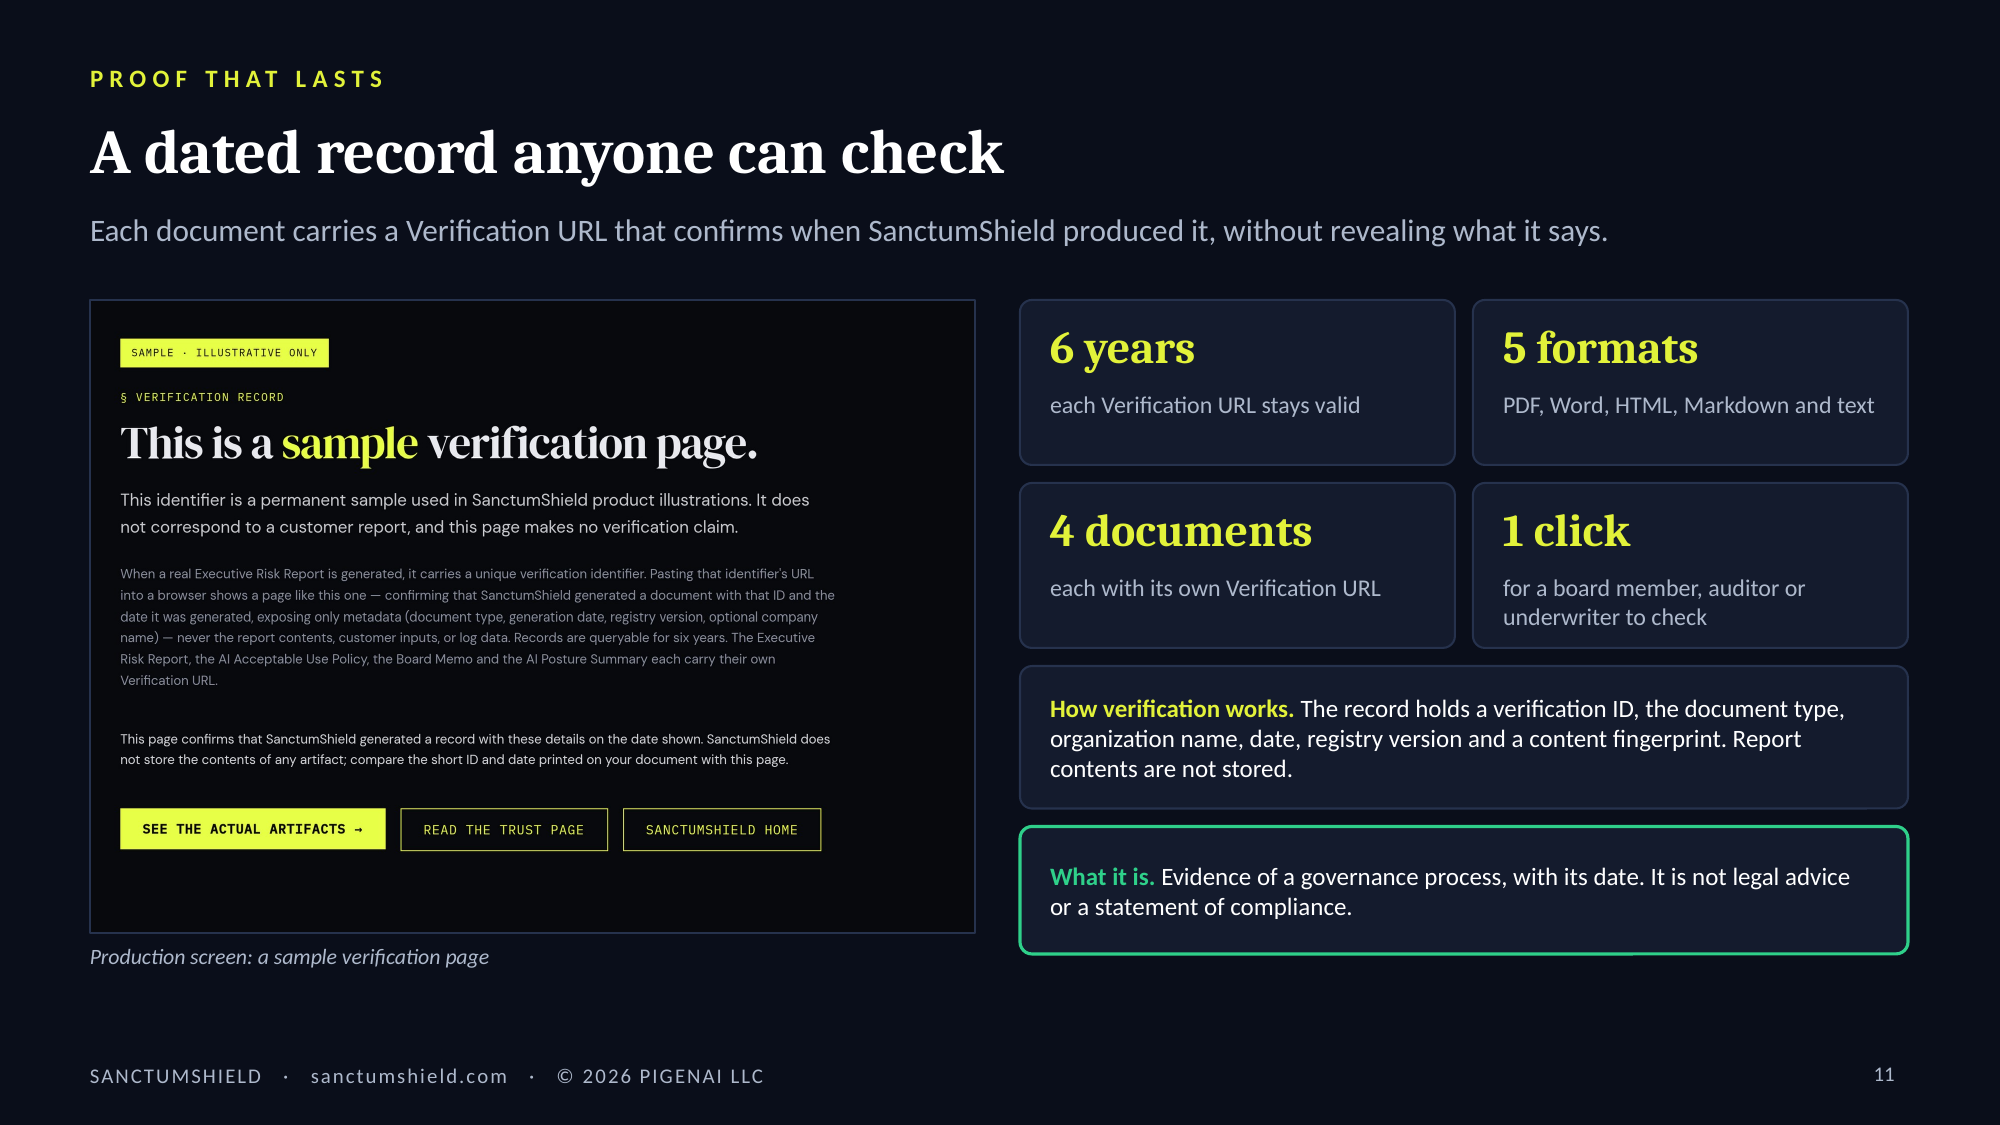
Your answers and your network logs are checked against a catalog of 130 AI tools and built-in AI features, and a registry of 118 known AI endpoints. Both are refreshed monthly.
Twelve frameworks inform the method. Seven are written into the policy text clause by clause today: the EU AI Act, HIPAA, GDPR, CCPA, SOC 2, the NIST AI RMF and ISO 27001. Five more are on the roadmap.
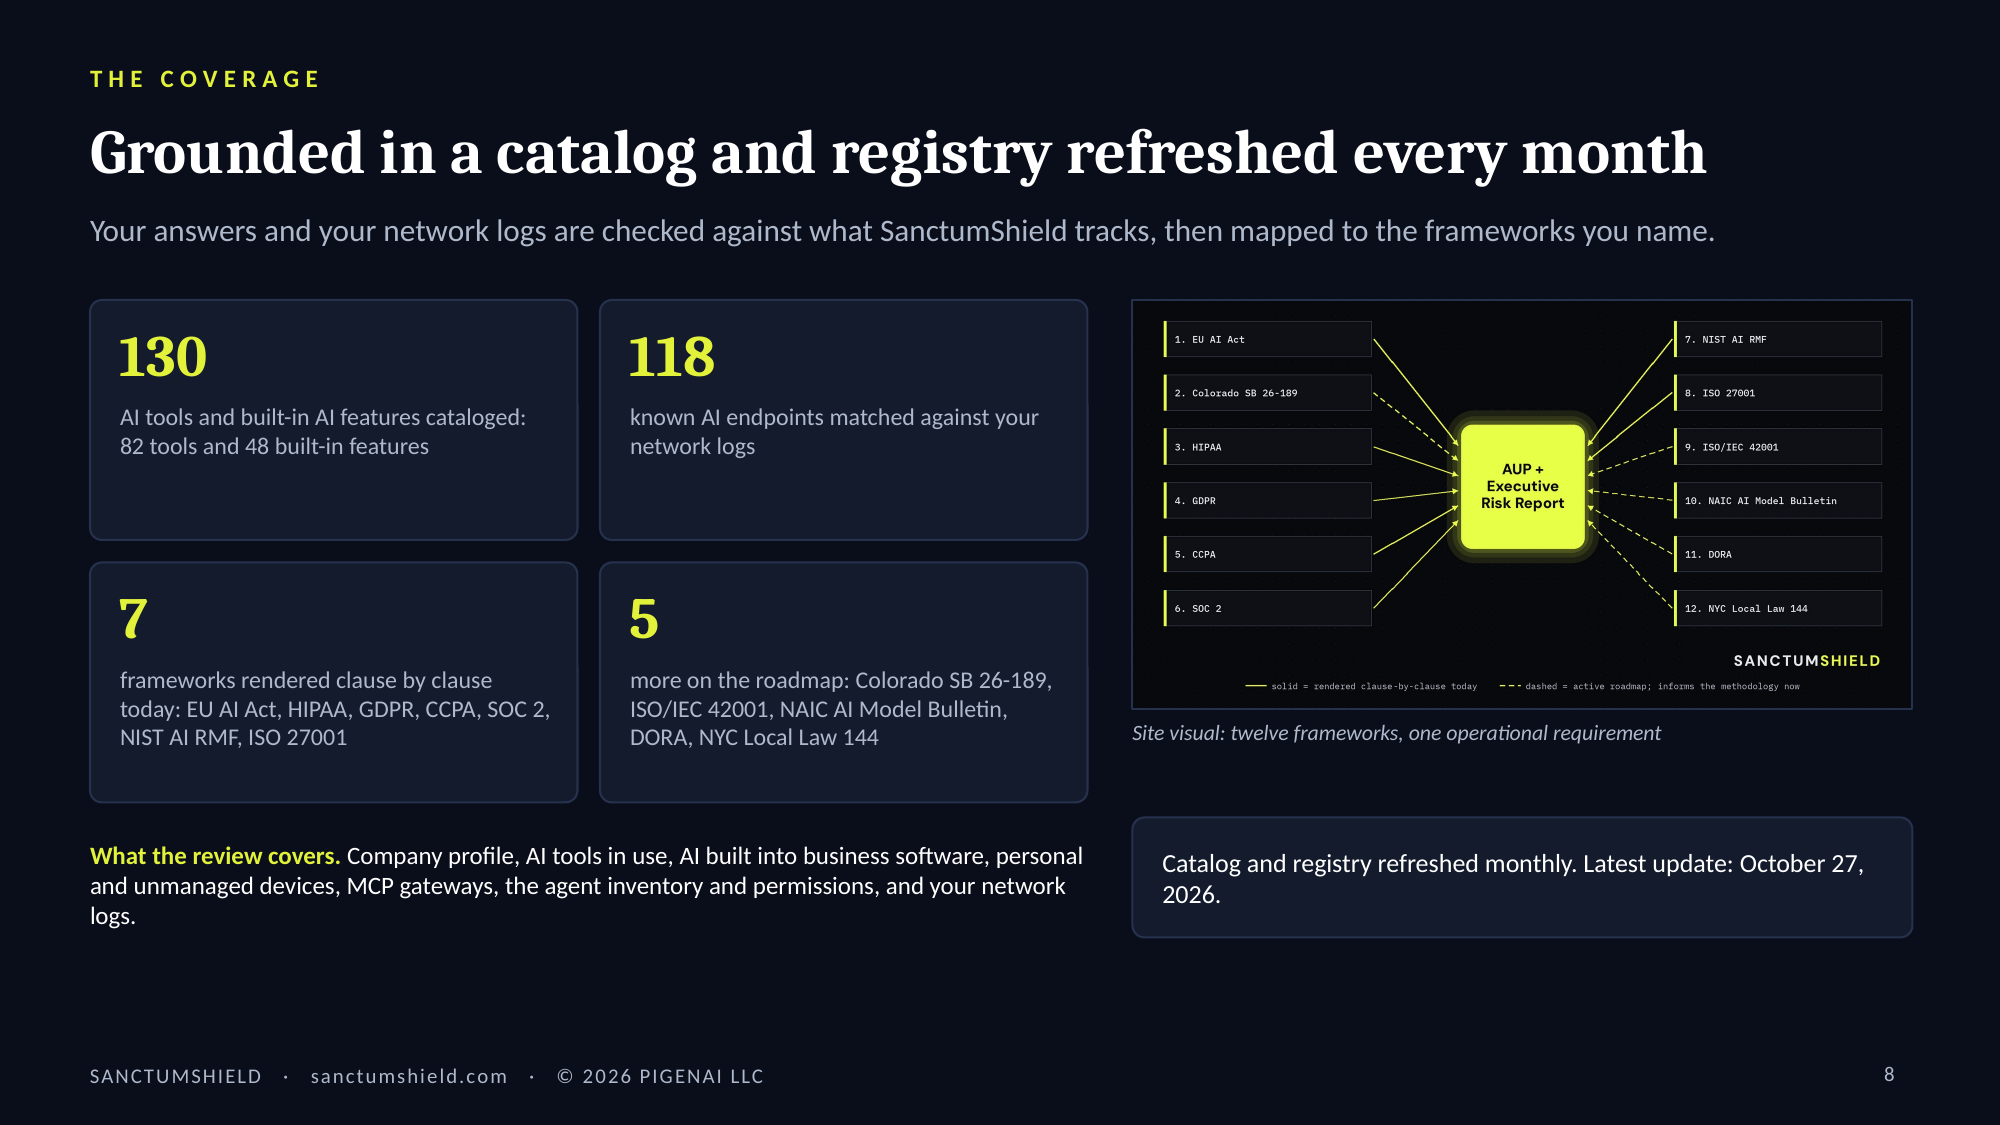
Agents are part of every review
A dedicated section records each agent: the platform it runs on, what it can do, who owns it, who can stop it, and when that stop was last tested. The AI Acceptable Use Policy includes a Deployed Agent Policy covering registration, an MCP server allowlist, a kill-switch, subagent authorization and spend ownership.
SanctumShield records who authorized each agent and on what terms. Runtime tools watch the agent run. The two work side by side.
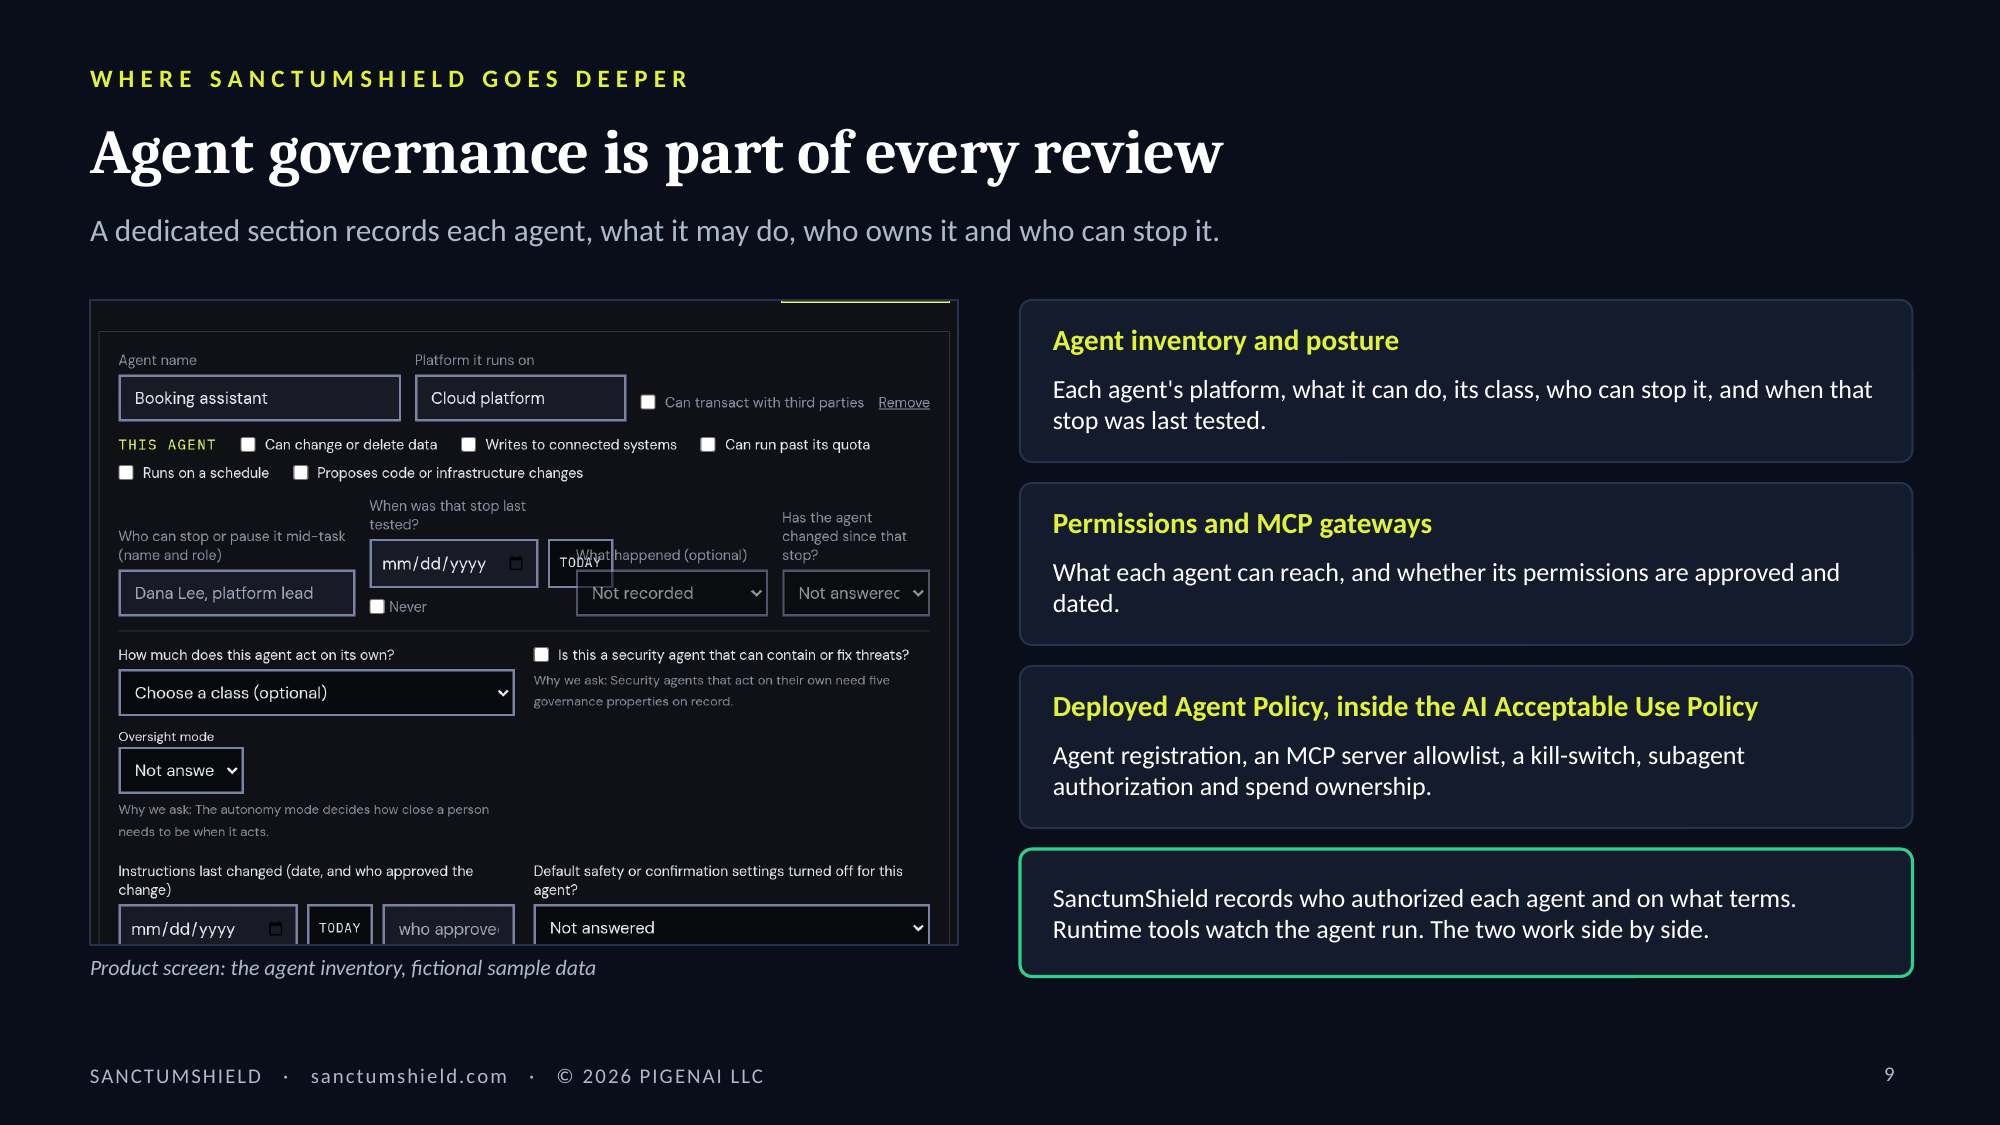
Answer, check, decide, share
The review runs in the browser, with nothing to install. Questions come one at a time, each with a short "Why we ask", and "Not sure" is a fine answer.
At the end you review every answer, then decide each open item: fix it, accept the risk, or decide later, with an owner and a date. Then you download all four documents in PDF, Word, HTML, Markdown or text.
The AI Governance Coach is there throughout, by voice or text.
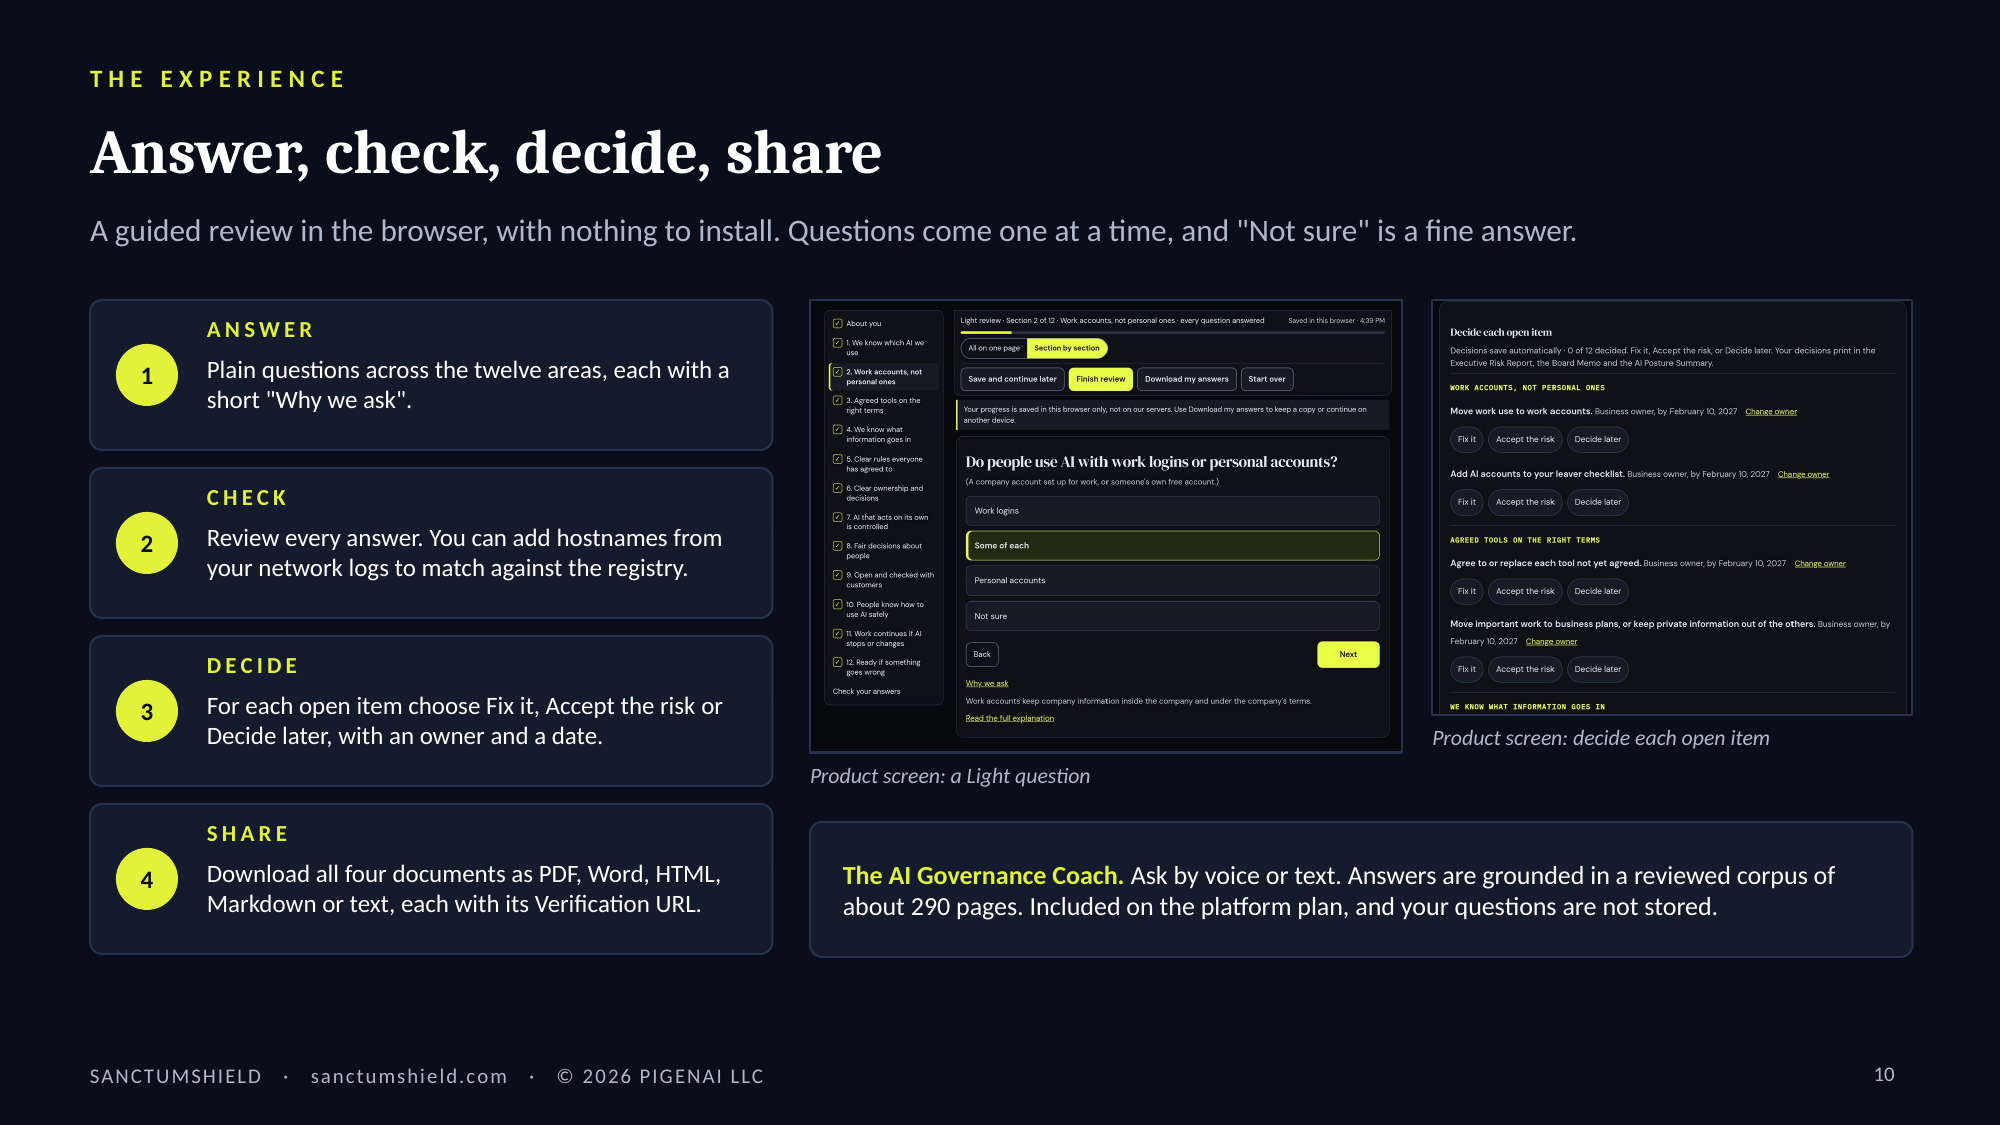
A record anyone can check
Each document's Verification URL confirms when SanctumShield produced it, without revealing what it says. The record holds a verification ID, the document type, the organization name, the date, the registry version and a content fingerprint. Each Verification URL stays valid for six years.
The record is evidence of a governance process, with its date. It is not legal advice or a statement of compliance.
What changes for each person in the room
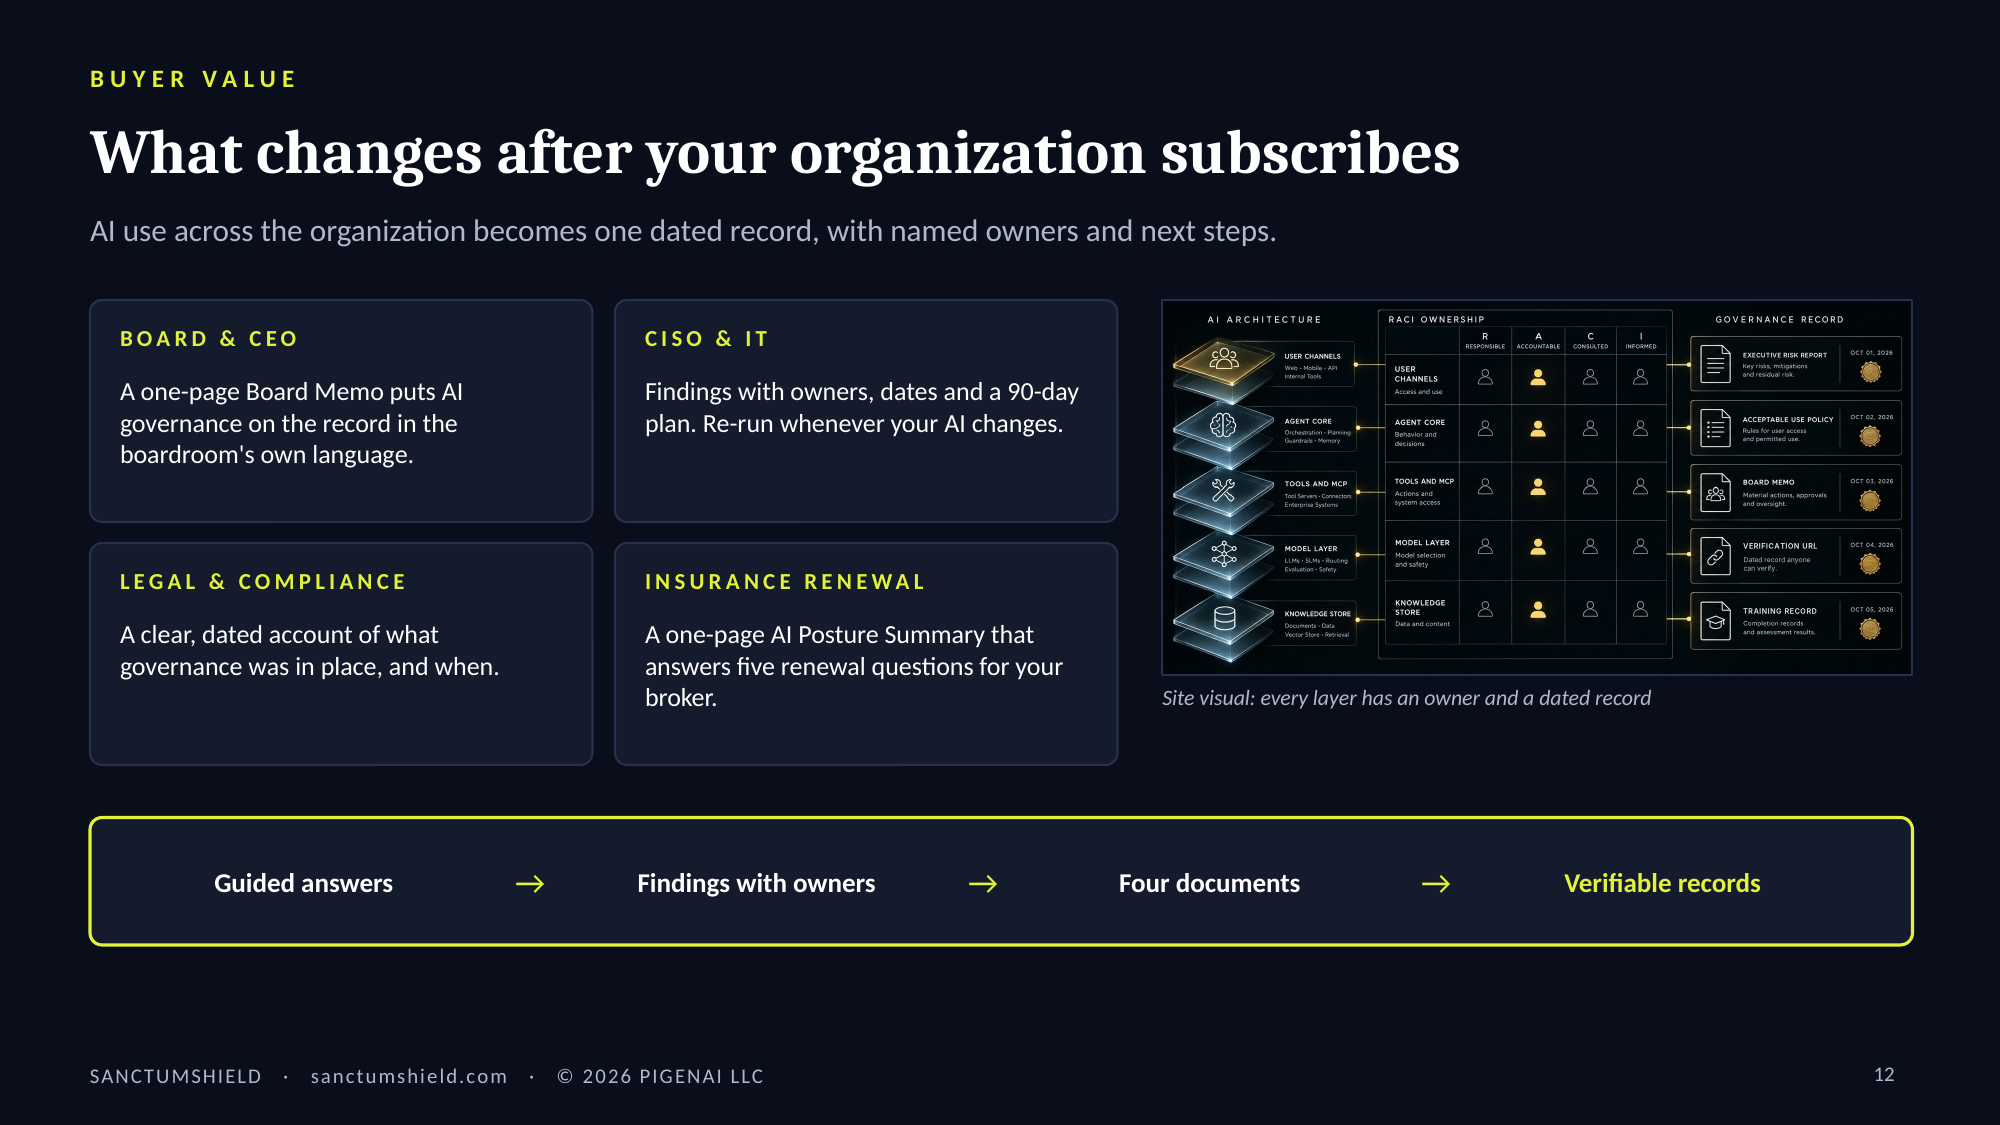
- Board and CEO. A one-page Board Memo puts AI governance on the record in the boardroom's own language.
- CISO and IT. Findings with owners, dates and a 90-day plan, re-run whenever your AI changes.
- Legal and compliance. A clear, dated account of what governance was in place, and when.
- Insurance renewal. A one-page AI Posture Summary that answers five renewal questions for your broker.
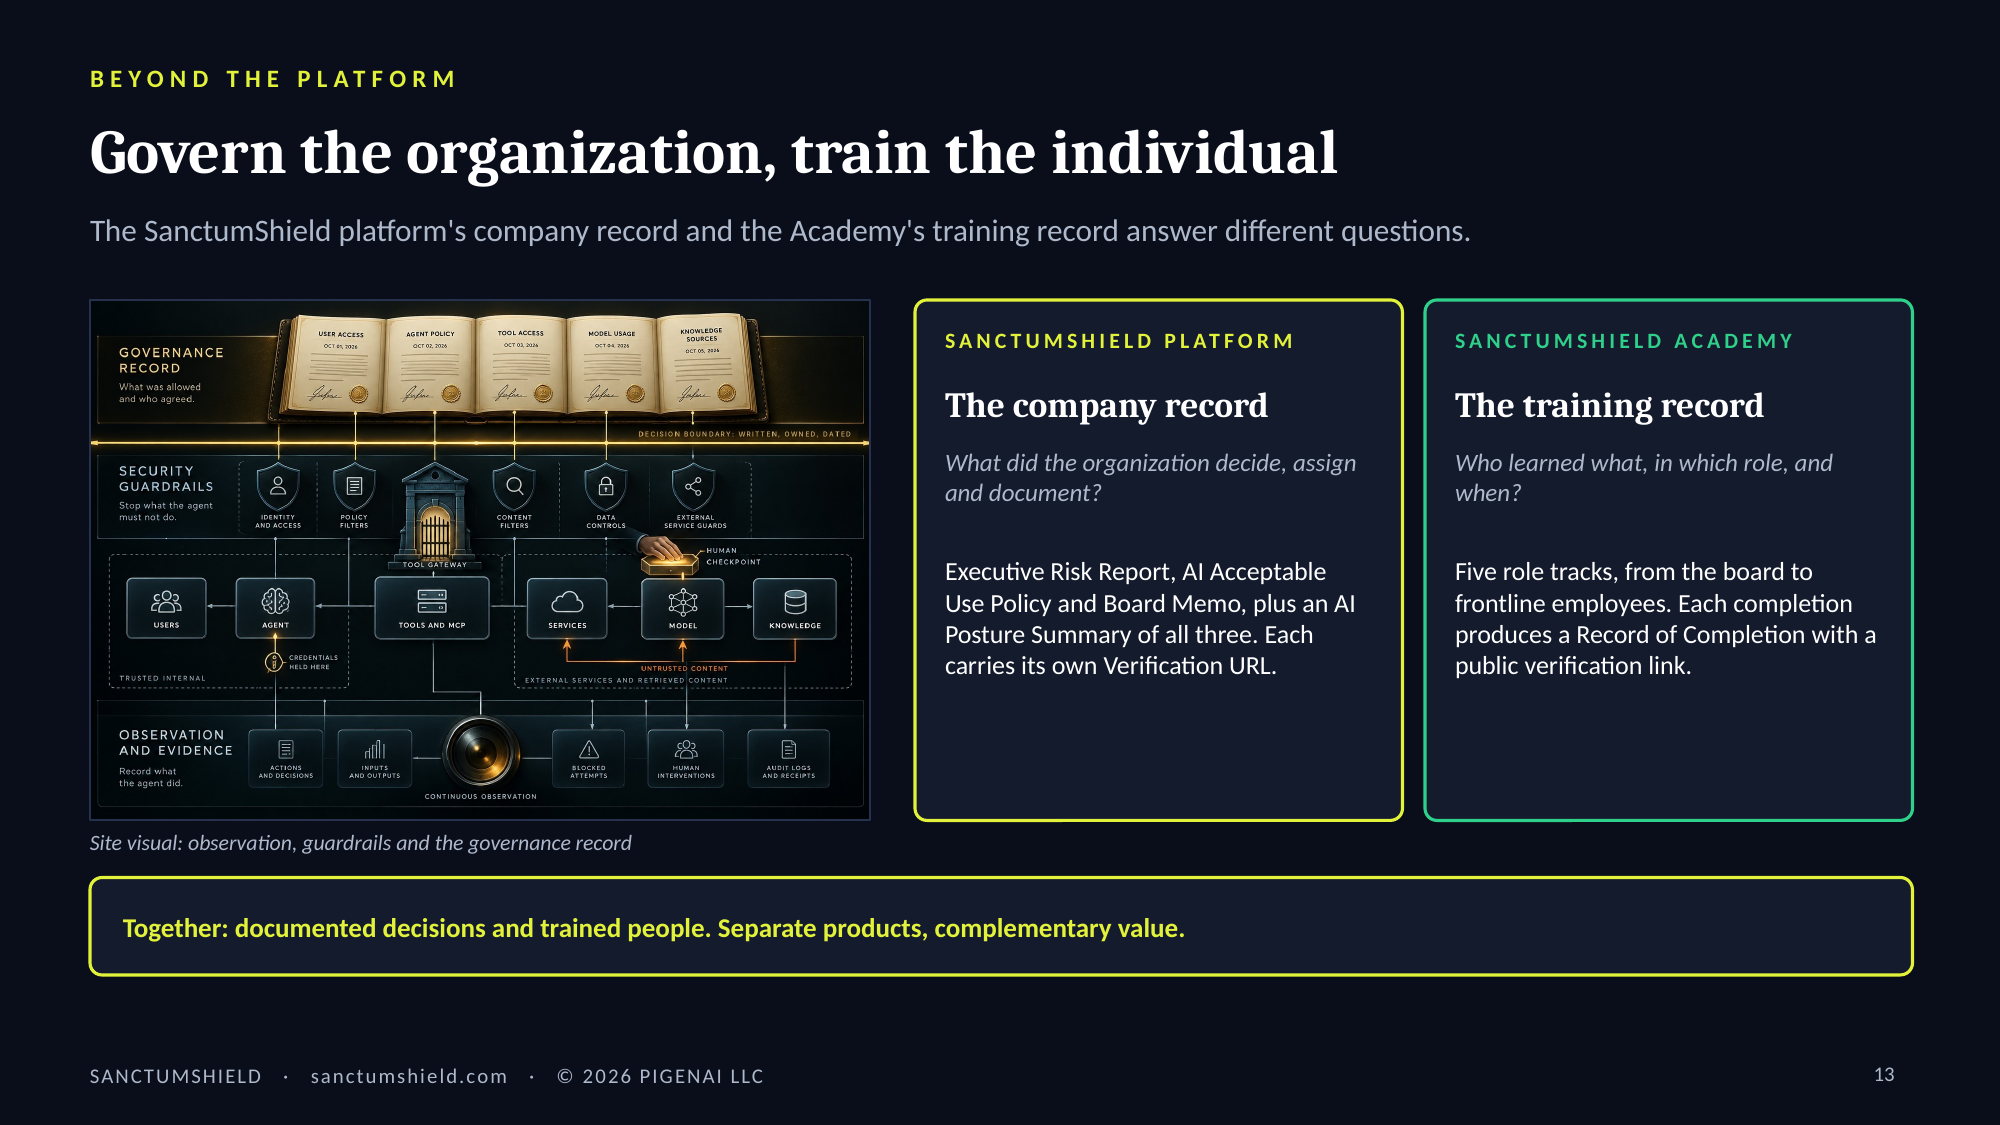
The company record and the training record
SanctumShield records what the organization decided, assigned and documented. SanctumShield Academy records who learned what, in which role, and when, with a Record of Completion for each person. They are separate products that fit together: documented decisions and trained people.
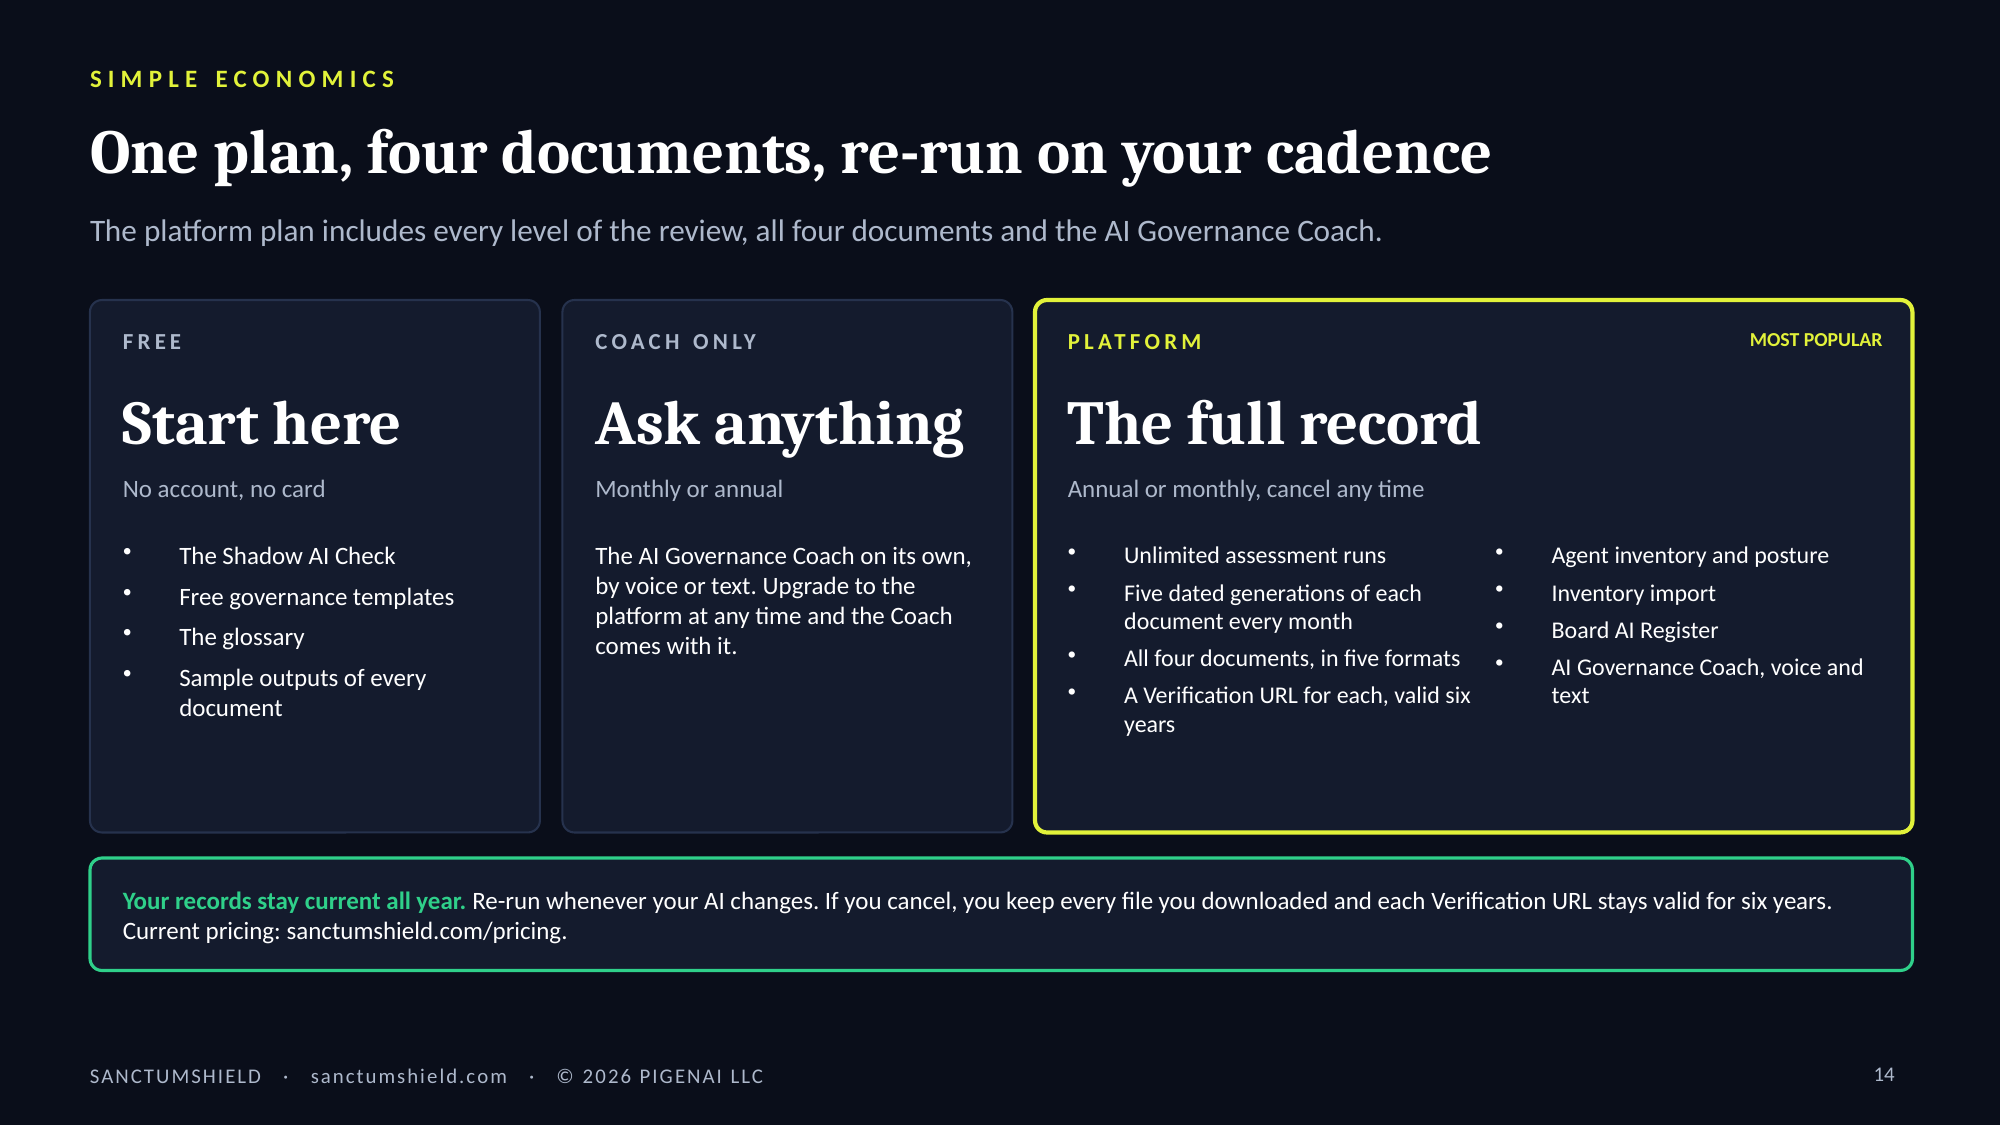
Plans
There are three ways to start.
| Plan | What it includes |
|---|---|
| Free | The Shadow AI Check, the governance templates, the glossary and sample outputs of every document. No account, no card. |
| Coach only | The AI Governance Coach on its own, by voice or text. Monthly or annual. |
| Platform | Unlimited assessment runs, all four documents in five formats, a Verification URL for each, the agent inventory, inventory import, the Board AI Register and the Coach. Annual or monthly. |
Current pricing is on the pricing page.
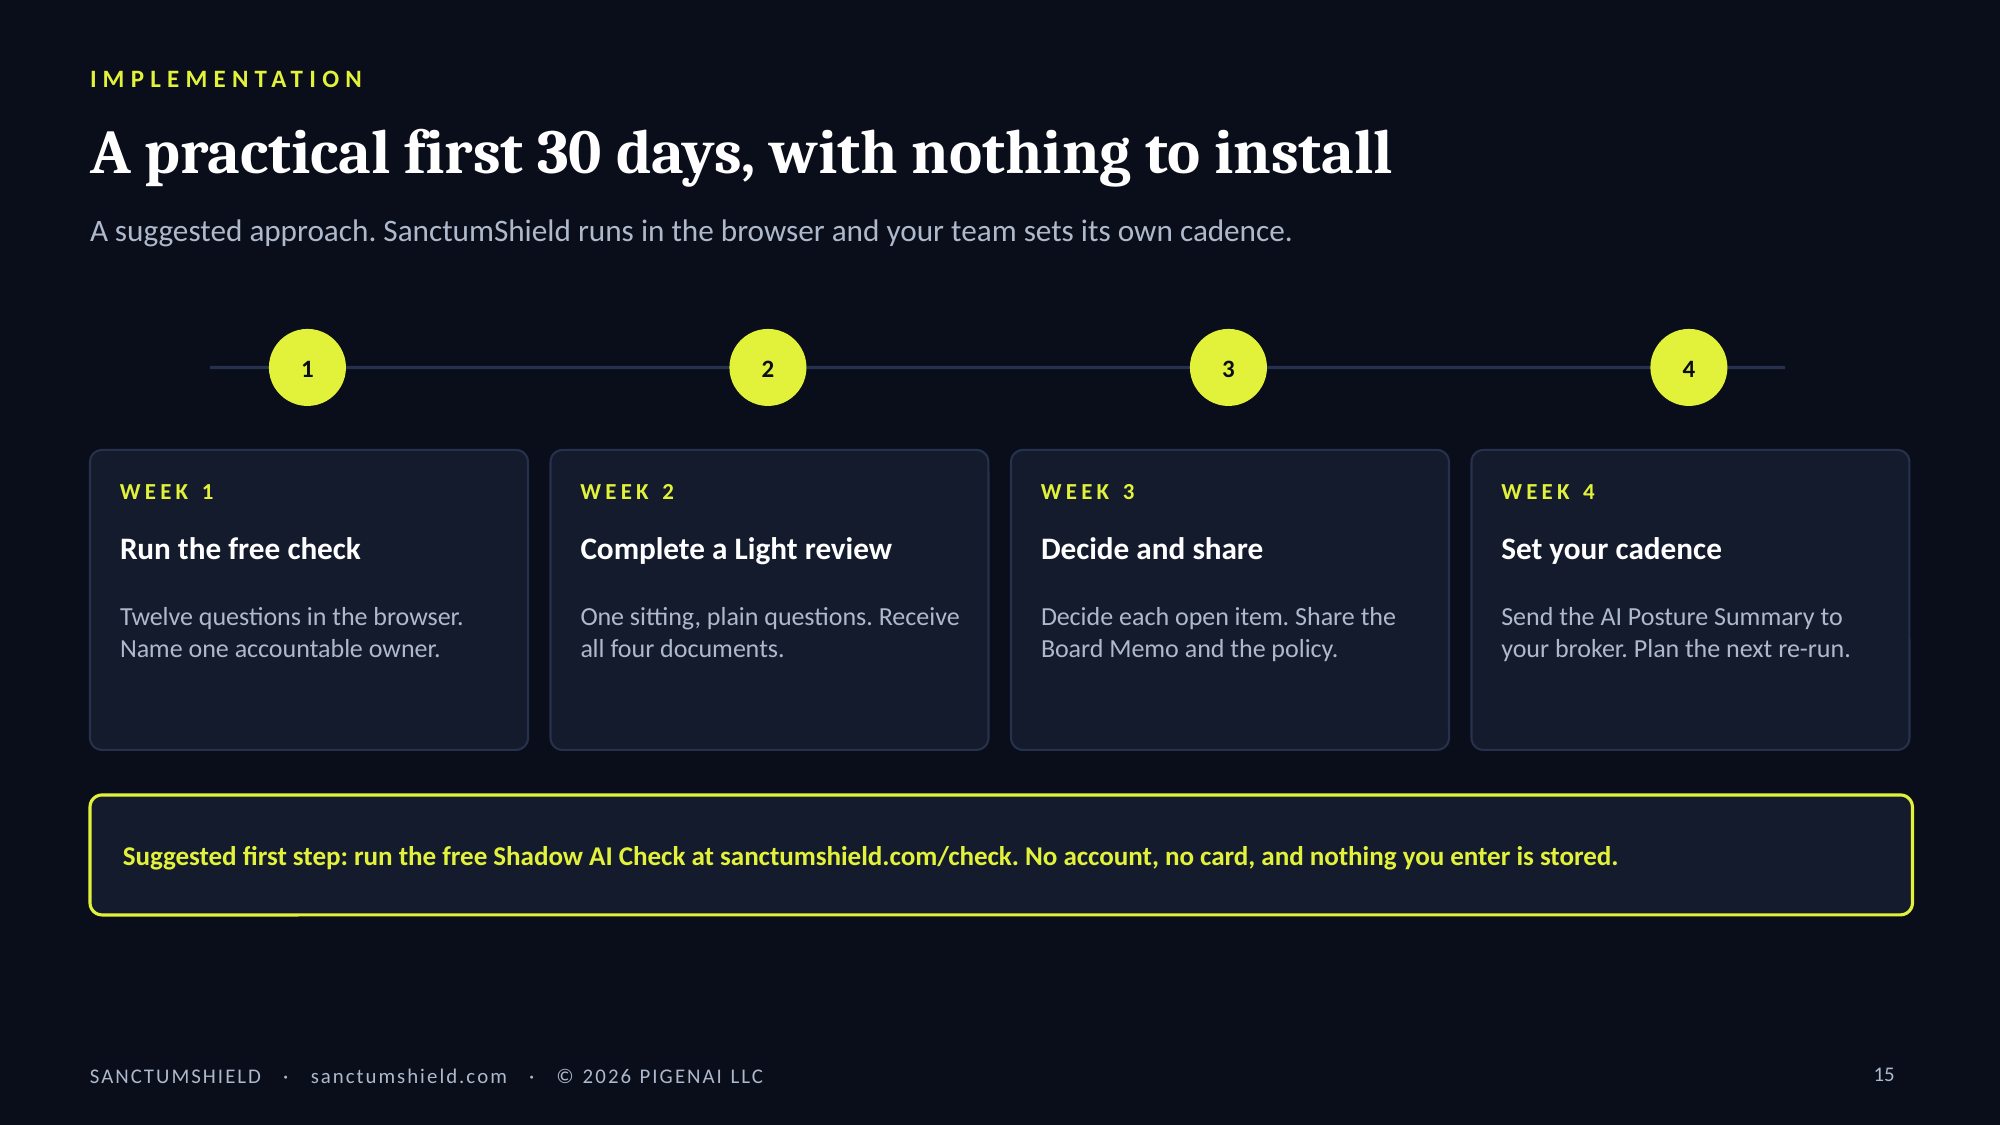
A practical first 30 days
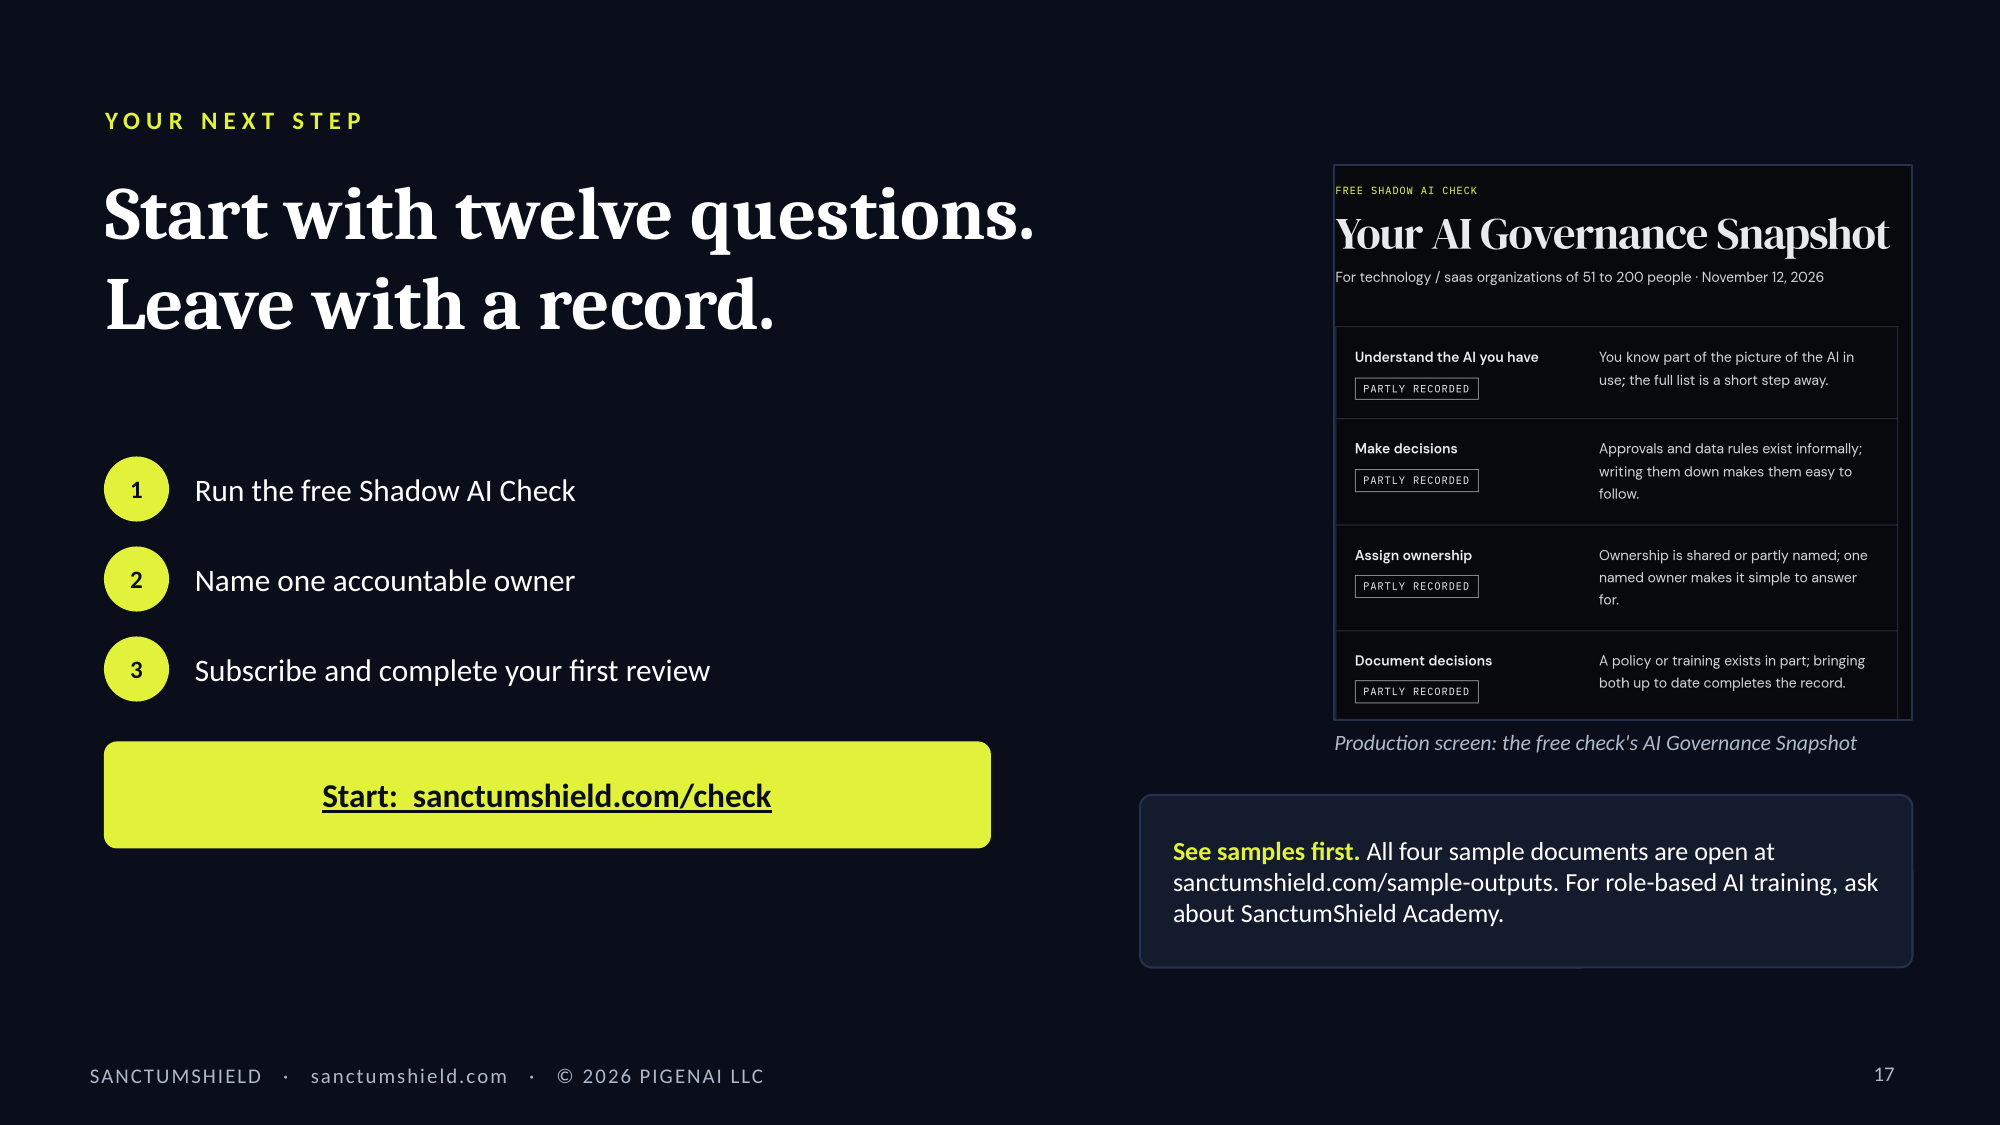
A suggested approach: run the free check and name one accountable owner in week one. Complete a Light review in week two and receive all four documents. Decide each open item and share the Board Memo and the policy in week three. In week four, send the AI Posture Summary to your broker and plan the next re-run.
Four questions buyers ask
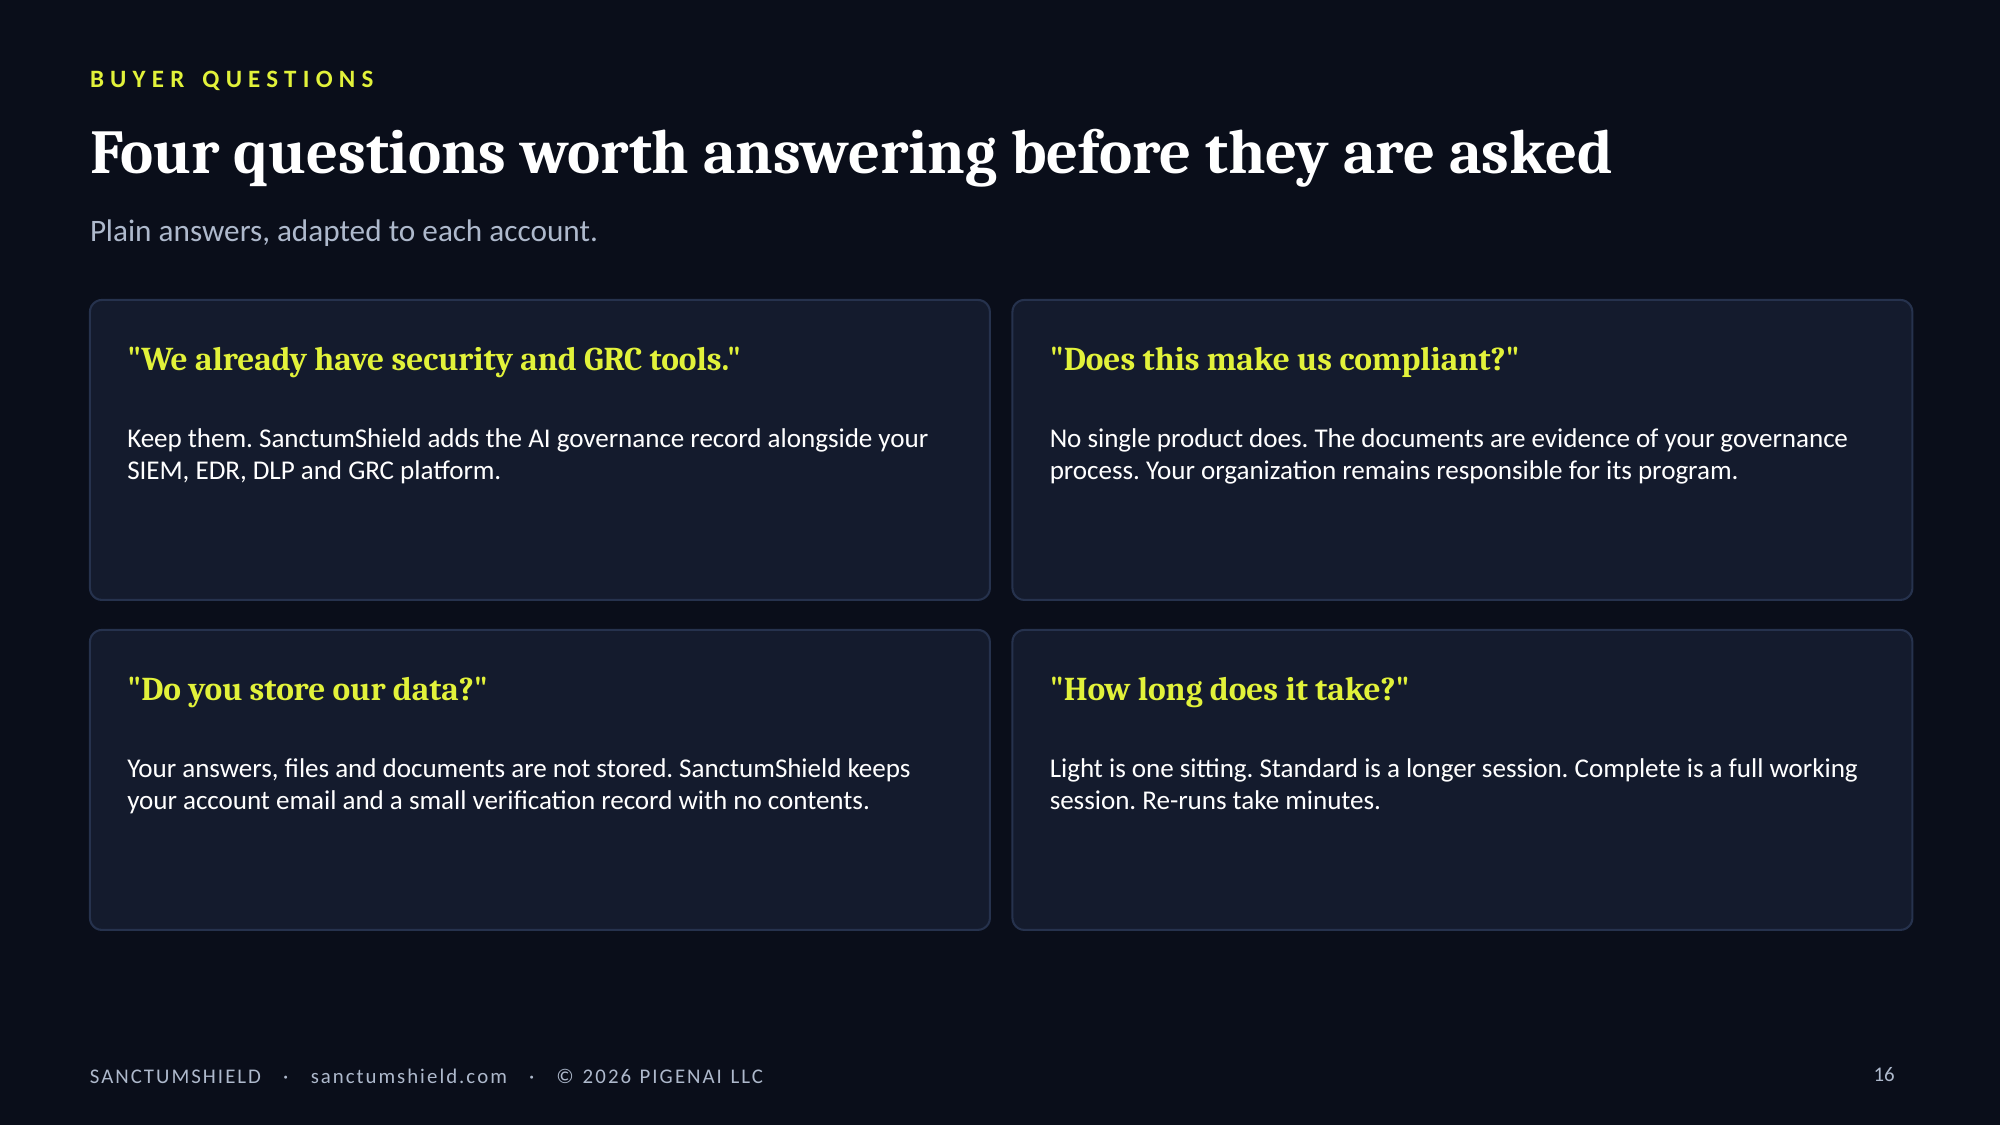
"We already have security and GRC tools." Keep them. SanctumShield adds the AI governance record alongside your SIEM, EDR, DLP and GRC platform.
"Does this make us compliant?" No single product does. The documents are evidence of your governance process, and your organization remains responsible for its program.
"Do you store our data?" Your answers, files and documents are not stored. SanctumShield keeps your account email and a small verification record with no contents.
"How long does it take?" Light is one sitting. Standard is a longer session. Complete is a full working session. Re-runs take minutes.
Getting started
Start with twelve questions. The free Shadow AI Check runs in your browser, needs no account, and stores nothing you enter. All four sample documents are open on the sample outputs page.
Sources
- Regulation (EU) 2024/1689 (EU AI Act), as amended by Regulation (EU) 2026/1744 (Digital Omnibus on AI).
- Colorado Senate Bill 26-189, signed May 14, 2026, with duties from January 1, 2027.
- SanctumShield: Why now, Pricing, Trust, Sample outputs.